One of the tricky parts of engineering in the physical world is making machines work with the available resources and manufacturing technologies. [Tom Stanton] has designed and made a couple of air-powered 3D printed engines but always struggled with the problem of air leaking past the 3D-printed pistons. Instead of trying to make an air-tight piston, he added a rubber membrane and a clever valve system to create a diaphragm air engine.
This GIF is worth 115 words
A round rubber diaphragm with a hole in the center creates a seal with the piston at the top of its stroke. A brass sleeve and pin protrude through the diaphragm, and the sleeve seals create a plug with an o-ring, while the pin pushes open a ball which acts as the inlet valve to pressurize an intermediate chamber. As the piston retracts, the ball closes the inlet valve, the outlet valve of the intermediate chamber is opened, forcing the diaphragm to push against the piston. The seal between the piston and diaphragm holds until the piston reaches its bottom position, where the pressurized air is vented past the piston and out through the gearbox. For full details see the video after the break.
It took a few iterations to get the engine to run. The volume of the intermediate chamber had to increase and [Tom] had to try a few different combinations of the sleeve and pin lengths to get the inlet timing right. Since he wanted to use the motor on a plane, he compared the thrust of the latest design with that of the previous version. The latest design improved efficiency by almost 200%. We look forward to seeing it fly!
The competition between Intel and AMD has been heating up in the last few years as Intel has released chips fabbed with their 14nm++ process and AMD has been using TMSC’s 7nm process. In the wake of the two semiconductor titans clashing, a debate between the merits of 14nm++ and 7nm has sprung up with some confusion about what those numbers actually measure. Not taking either number at their face value, [der8auer] decided to extract a transistor from both Intel’s and AMD’s latest offerings to try and shed some light.
Courtesy of WERBEVIDEO
Much of the confusion comes from the switch to the FinFET process. While older planar transistors could be thought of as largely 2d structures, FinFET’s are three dimensional. This means that the whole vertical fin can act as a gate, greatly reducing leakage. It is this fin or gate that [der8auer] is after. On each chip, a thin sliver from the L1 cache was chosen as caches tend to be fairly homogenous sections with transistors that are fairly indicative of the rest of the chip. Starting with a platinum gas intersecting with a focused ion beam on the surface of the chip, [der8auer] built a small deposit of platinum over several hours. This deposit protects the chip when he later cut it at an angle, forming a small lamella 100 micrometers long. In order for the lamella to be properly imaged by the scanning electron microscope, it needed to be even thinner (about 200 to 300nm).
Eventually, [der8auer] was ultimately able to measure the gate height, width, spacing, and other aspects of these two chips. The sheer amount of engineering and analysis that went into this project is remarkable and we love the deep dive into the actual gates that make up the processors we use. If you’re looking for a deep dive into the guts of a processor but perhaps at a more macro scale, why not learn about a forgotten Intel chip from the 1970s?
The Canon EOS R5 is a highly capable, and correspondingly very expensive, DSLR camera. Capable of recording video in 8K in a compact frame size, it unfortunately suffers from frustrating overheating issues. Always one to try an unconventional solution to a common problem, [Matt] decided to whip up a watercooling solution. What ensues is pure, top-notch engineering.
The watercooling setup is amusing, but the real star of the show is the custom copper heatsink that transforms the camera’s performance without spoiling its practicality.
Upon its original release, Canon had the R5 camera simply shut off on a 20 minute timer when recording 8K video. When the userbase complained, an updated firmware was released that used an onboard sensor and would only shutdown when excessive temperatures were reached. Under these conditions, the camera could record for around 25 minutes at 20 °C. [Matt] set about disassembling the camera to investigate, figuring out that the main processor was the primary source of heat. With a poor connection to its heatsink and buried under a power supply PCB, there simply wasn’t anywhere for heat to go, leaving the camera to regularly overheat and take hours to cool down.
After whipping up an amusing but impractical watercooling solution and verifying it allowed the camera to record indefinitely, [Matt] set about some proper thermal engineering. A custom copper heatsink was produced for inside the camera, bonded directly to the processor and DRAM with thermal paste instead of poor-quality thermal tape. This then directs heat out through the plastic back of the camera. In cool environments, this is enough to allow the camera to record continuously. In warmer environments, simply adding a small fan to the back of the camera was enough to keep things operational indefinitely.
[Matt] finishes the video by pointing out that Canon could have made the camera far more useful for videographers by simply investing a little more time into the camera’s cooling design, while also generating more profits by selling a cooling accessory for extended recording. We’ve seen some of [Matt’s] work before too, such as this DIY 4K projector build. Video after the break.
Like many modern smart home gadgets, Belkin’s Wemo brand of smart plugs has a tendency to phone home every time you turn on a lamp. [Gigawatts] wasn’t having it, so they figured out how to flash the device with OpenWRT and replicated its original functionality with a web interface. Unfortunately this stopped working after awhile, and rather than trying to diagnose the issue, it seemed the time would be better spent simplifying the whole thing.
As [Gigawatts] explains, there are actually two separate boards inside the Wemo plug. One holds the relay to do the high-voltage switching, and the other provides the control. They are linked with a three wire connector, making it exceptionally simple to swap out the original controller for something different. The connector supplies 5 V and ground, all you’ve got to do is pull the third wire high to flick the switch.
While the ESP8266 probably would have been the first choice for many a Hackaday reader, [Gigawatts] actually went with the Moteino, a low-power Arduino compatible board with integrated RFM69 transceiver. With an LED to indicate status and a few lines of code tweaked, the Moteino got this once WiFi-only smart plug speaking a new language.
There’s some debate over how effective smart plugs are from an energy efficiency standpoint, but even if this reborn Wemo doesn’t help [Gigawatts] save much power, at least it won’t be blabbing about everything to a third-party.
You hold in your hand a circuit board from a product you didn’t make. How does the thing work? What a daunting question, but it’s both solvable and approachable if you know what you’re doing. The good news is that Eric Schlaepfer knows exactly what he’s doing and boiled down the process of reverse engineering printed circuit boards into this excellent workshop. It was presented live during the 2020 Hackaday Remoticon, and the edited video, which you’ll find below, was just published. Slides for the talk have been published on the workshop project page.
Eric tackles the challenge in two parts. The first is to generate a bill of materials by harvesting as much information as possible, and then to fill in the rest of the details with liberal use of search engines and datasheets. He pulls everything into a spreadsheet, with columns for the parts designators printed on the board (U1, R53, C4, etc.), package type which you kind of get the hang of with experience, topmark (printed on the parts), and the part number gleaned from the above.
The next step is to reverse engineer the circuit board itself by taking high-resolution images, sometimes removing parts from the board to do so, and a schematic with every part you noted from the first step but no connected traces. Eric demonstrates how to use GIMP image editor to map out traces, adding nets in the schematic as he begins to solve pieces of the puzzle. As he draws the traces on their own layer, switching back and forth between images of the board immediately begins to demystify the connections split between the two layers.
He certainly makes it look both fast and easy, and for him it is. The key is getting a few of these under your belt until you can lean on experience to unstick the sticking points. But whether this is your very first rodeo, or you’re a seasoned veteran, the methodical approach is admirable and a welcomed addition to everyone’s skill set.
Let’s Encrypt was founded in 2012, going public in 2014, with the aim to improve security on the web. The goal was to be achieved by providing free, automated access to SSL and TLS certificates that would allow websites to make the switch over to HTTPS without having to spend any money.
Hundreds of millions of sites rely on Let’s Encrypt for their HTTPS certificate needs. HTTPS security helps protect sites and users, and makes it harder for malicious actors to steal private information.
When Let’s Encrypt first went public in early 2016, they issued their own root certificate, by the name ISRG Root X1. However, it takes time for companies to include updated root certificates in their software, so until recently, all Let’s Encrypt certificates were cross-signed by an IdenTrust certificate, DST Root X3. This certificate had been around much longer, and was already supported by the vast majority of OSes and browsers in regular use. This allowed Let’s Encrypt to hit the ground running while they waited for the majority of software to support their own root certificate.
The problem looming on the horizon is the expiration of DST Root X3, on September 1, 2021. Of course, for those running up-to-date operating systems and browsers, there’s no major issue. But for those on platforms that haven’t been updated since 2016 or so, and don’t support the ISRG Root X1 certificate, things will break. This affects any secure communication that uses their certificates, whether it be browsing websites with HTTPS enabled or making connections over SSL or SFTP.
The company notes that perhaps the biggest area of concern is the Android handset market. As most telecommunications networks customise Android software, along with the handset manufacturer themselves, it takes coordination between many organisations to put out an OS update for an Android phone. There’s also little financial incentive for companies to support phones that have already been sold. Thus, many users find themselves locked out from OS updates entirely as networks or manufacturers simply neglect to do the work.
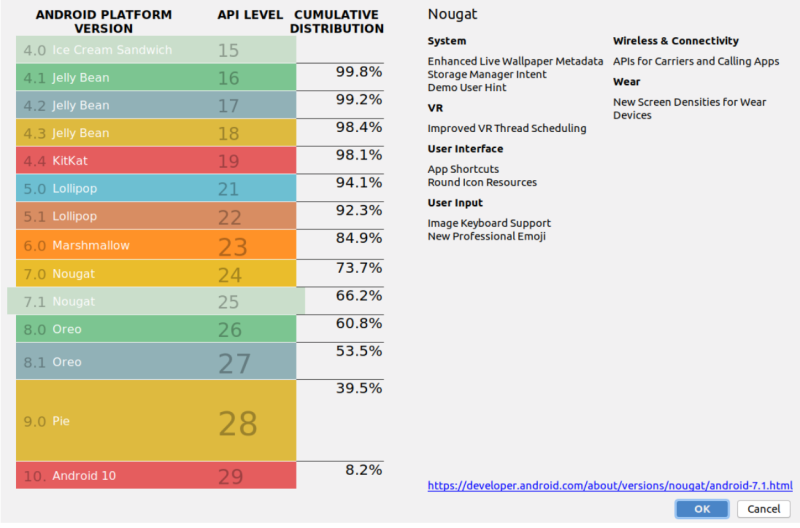
Data on the Android installed base, as of September 2020.
Android users on versions older than 7.1.1 are the ones who will face issues when DST Root X3 expires on September 1 next year. Based on recent statistics, these users make up roughly a third of the Android userbase – a significant number. With a conservative estimate pegging Android users as a whole making up approximately 80% of the total smartphone installed base, and around 3 billion smartphone users worldwide, back of the envelope calculations show us that leaves around 750 million users that could have issues in the coming year.
Of course, workarounds are possible. While the Android OS, and presumably web browser, are long out of date, there’s nothing stopping users installing newer software that supports the ISRG Root X1 certificate. Firefox is available as a browser on the platform, and packs in its own list of trusted root certificates, so is a useful workaround for day to day web use. For developers, it’s possible to include ISRG Root X1 as a trusted certificate within an individual app, and discussions are ongoing among those taking to this route. After all, adding an new trusted certificate is just putting a file in a directory, but you need root permissions to do so, which on locked Android phones means a jailbreak.
Let’s Encrypt could also seek a cross-signature from another Certificate Authority, similar to when they started out. However, Certificate Authorities take on some responsibility for the certificates they sign, and it’s unlikely that another CA would wish to shoulder that burden for Let’s Encrypt. Particularly, as the entity is a non-profit, there is little money to be made. As a major pillar in the Internet’s shift towards HTTPS encryption as the norm, Let’s Encrypt consider it important that the project stand on its own, rather than relying on other for-profit organisations. Given that their root certificate is now widely recognised, outside these edge cases from 2016 and earlier, that seems like a sound decision.
With security on the Internet now more important than ever, this is a problem that isn’t going away. In order to play nice with all the other computers on the global network, regular updates are simply the cost of doing business. The benefit of having an open certificate provider like Let’s Encrypt around is that their transparency as to the issues and clear communication gives web hosts, developers, and end users more time to deal with the coming changes.
Going back to classic games can be a difficult experience. The forward passage of time leaves technology to stagnate, while the memories attached to those old games can morph in mysterious ways. Therein lies the problem with how you remember a game playing versus the reality of how it actually does. Developer [Jorge] saw that situation arising around Zelda II: The Adventure of Link, and it inspired him to create the Zelda II Redux ROM hack.
Years in the making, Zelda II Redux takes a relatively light-handed approach to revising the original NES game. Graphical enhancements include: a reworked HUD complete with the series’ tradition of hearts, animated enemy icons in the over world, a new title screen, and giving Link the shield from the Famicom Disk System release’s box art. Text speed has been increased and a revised translation of the Japanese script has been incorporated. Under the hood, all sorts of boss battles have been re-balanced while casting magic spells doesn’t require multiple return trips to the pause menu. Though Zelda II Redux’s most important feature may be the inclusion of manual saving via “Up + A” on the pause menu. There are also a whole host of other changes Zelda II Redux incorporates in order to bring Link’s second adventure more inline with the rest of the Legend of Zelda series that can be found on the project’s change log.
To play Zelda II Redux requies an IPS patching program, like LunarIPS, along with a clean dumped image of Zelda II: The Adventure of Link. Dumping NES cartridges is easier than ever these days due to many cartridge dumper devices being plug-and-play over USB. A successfully patched ROM file can be played in an emulator or on actual NES hardware through a flash cart. A video of a tool-assisted speedrun has been included below, so there may be some new strategies to employ.
More people working from home has had an impact on the cost and availability of USB webcams, so [Jeff Geerling] got around the issue with a DIY solution that rang in around $100. It consists of a Raspberry Pi and HQ camera module acting as a USB webcam, and there is no messy streaming of ffmpeg over the network masquerading as a camera device or anything. It works just as a USB camera should.
[Jeff] chose a Raspberry Pi Zero and HQ camera module for his unit, making a tidy package that might not be quite as small as commercial webcams, but is certainly perfectly respectable as a USB camera. That being said, there are a few drawbacks, namely the lack of a microphone or autofocus, latency issues at higher resolutions, and the need to shut down the Pi cleanly.
Check out the GitHub repository for everything needed to set up your own, including a complete hardware list and some options for mounting. [Jeff] also tested whether the camera would work with the new keyboard-embedded Raspberry Pi 400, and it absolutely does. Embedded below is a video walkthrough and demonstration of the whole project, so check it out.
Refining precious metals is not as simple as polishing rocks that have been dug out of the ground. Often, complex chemical processes are needed to process the materials properly or in high quantities, but these processes leave behind considerable waste. Often, there are valuable metals left over in these wastes, and [NerdRage] has gathered his chemistry equipment to demonstrate how it’s possible to recover these metals.
The process involved looks to recover copper and nitric acid from copper nitrate, a common waste byproduct of processing metal. While a process called thermal decomposition exists to accomplish this, it’s not particularly efficient, so this alternative looks to improve the yields you could otherwise expect. The first step is to react the copper nitrate with sulfuric acid, which results in nitric acid and copper sulfate. From there, the copper sulfate is placed in an electrolysis cell using a platinum cathode and copper anodes to pass current through it. After the process is complete, all of the copper will have deposited itself on the copper electrodes.
The other interesting thing about this process, besides the amount of copper that is recoverable, is that the sulfuric acid and the nitric acid are recoverable, and able to be used again in other processes. The process is much more efficient than thermal decomposition and also doesn’t involve any toxic gasses either. Of course, if collecting valuable metals from waste is up your alley, you can also take a look at recovering some gold as well.
A solar eclipse is coming up in just a few weeks, and although with its path of totality near the southern tip of South America means that not many people will be able to see it first-hand, there is an opportunity to get involved with it even at an extreme distance. PhD candidate [Kristina] and the organization HamSCI are trying to learn a little bit more about the effects of an eclipse on radio communications, and all that is required to help is a receiver capable of listening in the 10 MHz range during the time of the eclipse.
It’s well-known that certain radio waves can propagate further depending on the time of day due to changes in many factors such as the state of the ionosphere and the amount of solar activity. What is not known is specifically how the paths can vary over the course of the day. During the eclipse the sun’s interference is minimized, and its impact can be more directly measured in a more controlled experiment. By tuning into particular time stations and recording data during the eclipse, it’s possible to see how exactly the eclipse impacts propagation of these signals. [Kristina] hopes to take all of the data gathered during the event to observe the doppler effect that is expected to occur.
The project requires a large amount of volunteers to listen in to the time stations during the eclipse (even if it is not visible to them) and there are only a few more days before this eclipse happens. If you have the required hardware, which is essentially just a receiver capable of receiving upper-sideband signals in 10 MHz range, it may be worthwhile to give this a shot. If not, there may be some time to cobble together an SDR that can listen in (even an RTL-SDR set up for 10 MHz will work) provided you can use it to record the required samples. It’s definitely a time that ham radio could embrace the hacker community.
Are you wondering if it’s time to replace your car’s clutch? From grinding noises to difficulties getting into gear, there are plenty of signs that your clutch needs some extra attention. You can find clutches for sale, as well as automotive service providers, on Junk Mail.
What is a clutch and how does it work?
A
clutch is a mechanical device that plays an important role in the operation of
your car. The clutch functions to engage and disengage two rotating shafts. One
of the shafts is connected to the engine and the other shaft is responsible for
the power output.
The main parts of the clutch include the following:
Cover
plate
Pressure
plate
Driven
plate
Release
bearing
If
you live in the city where you’re faced with traffic on a regular basis, it’s
likely that your car’s
clutch will wear down quicker. Frequent stopping and starting can have a
negative impact on the lifespan of your clutch. Pulling heavy loads is also likely
to wear your car’s clutch
down.
5 signs that you need to replace your car’s clutch
Clutch slippage
If the
engine races but your vehicle is slow to take off, it’s an indication of a worn-out
clutch. It’s likely that the friction material has worn away so that it’s
difficult for the power to be transferred to the transmission. If this is the
case, you’ll need to replace the disc to get your vehicle back into shape.
However, there are other culprits of clutch slippage, which include problems
with the clutch linkage as well as a damaged pressure plate. A damaged motor
mount can also be the cause of this problem.
Getting into gear is difficult
Changing
gears can be problematic if your clutch isn’t in good condition, but issues
with changing gears could also be due to problems with the linkage adjustment,
a damaged clutch plate or a damaged cylinder fork.
Soft clutch
If
your clutch feels spongy, it’s advisable to have it checked out as soon as
possible. Another telltale sign of a clutch problem is if your car’s clutch shudders.
This issue is particularly noticeable when you’re travelling at low speeds. A
shuddering clutch can mean that there are impurities interfering with the
clutch plate or that the clutch plate needs to be replaced.
Grinding sounds
If
you notice grinding sounds when you push down the clutch, it could be a sign
that the clutch is worn. Faulty bearings could also be the culprit. It’s
important to deal with this problem as soon as possible because bearings are
cheap to replace but if you continue to drive with damaged bearings it can lead
to more expensive problems later.
How to make your car’s clutch last longer
Save
time and money by taking good care of your clutch. Clutches are a sensitive and
vital part of your vehicle, so it’s essential to know how to extend their
lifespan.
Don’t
apply pressure to the clutch while you’re driving unless you’re changing gears.
Even resting your foot on the clutch can create pressure that speeds up the
wear and tear of your clutch.
Reduce
the speed of your vehicle slowly and steadily before you come to a robot or
stop sign. Likewise, take off slowly and steadily rather than pretending you’re
on a racetrack.
Make
use of your parking brake when you’re taking off on an incline so that you can
avoid putting strain on your clutch.
Don’t
engage your clutch to assist with braking.
Photo Source – www.pixabay.com
Now that you know how to maintain your car’s clutch properly, you can keep your car in good shape. Find clutches for sale on Junk Mail and enjoy great savings.
[Billy] was no fan of doing the dishes, but also found commercial solutions lacking. The options on the market simply didn’t fit his cookware and flatware. Instead of compromising, he set out to build a dishwasher of his own design.
The build consists of a whole heap of hardware all lumped in a sizeable plastic tub. A washing machine solenoid lets water into the system, and it’s heated by an element in the base of the tub. It’s then pumped through a garden sprinkler head to give the dishes a good all-over spraying. At the end of a wash cycle, the drain pump then dumps the water to let everything dry off. An ESP8266 and a bank of relays are in place to run the show, with the user selecting wash programs via buttons and a small screen.
[3DprintedLife] sure does hate bread crust. Not the upper portion of homemade bread, mind you — just that nasty stuff around the edges of store-bought loaves. Several dozen hours of CAD later, [3DprintedLife] had themselves a crust-cutting robot that also chops vegetables.
This De-Cruster 9000 is essentially a 2-axis robotic guillotine over a turntable. It uses a Raspberry Pi 4 and OpenCV to seek and destroy bread crusts with a dull dollar store knife. Aside from the compact design, our favorite part has to be the firmware limit switches baked into the custom control board. The stepper drivers have this fancy feature called StallGuard that constantly reads the back EMF to determine the load the motor is under. If you have it flag you right before the motor hits the end of the rail and stalls, bam, you have a firmware limit switch. Watch it remove crusts and chop a lot of carrots with faces after the break.
WiFi just isn’t very good at going through buildings. It’s fine for the main living areas of an average home, but once we venture towards the periphery of our domains it starts to become less reliable. For connected devices outside the core of a home, this presents a problem, and it’s one Amazon hope to solve with their Sidewalk product.
It’s a low-bandwidth networking system that uses capability already built into some Echo and Ring devices, plus a portion of the owner’s broadband connection to the Internet. The idea is to provide basic connectivity over longer distances to compatible devices even when the WiFi network is not available, but of most interest and concern is that it will also expose itself to devices owned by other people. If your Internet connection goes down, then your Ring devices will still provide a basic version of their functionality via a local low-bandwidth wide-area wireless network provided by the Amazon devices owned by your neighbours.
I Can See Your Amazon Ring From Here
It looks so harmless, doesn’t it. Amin, CC BY-SA 4.0
The massive online retailer and IoT cloud provider would like to open up a portion of your home broadband connection via your home security devices over a wireless network to other similar devices owned by strangers. In the Amazon literature it is touted as providing all sorts of useful benefits to Ring and Echo owners, but it has obvious implications for both the privacy of your data should it be carried by other people’s devices, and for the security of your own network when devices you don’t own pass traffic over it. For the curious there’s a whitepaper offering more insights into the system, and aside from revealing that it uses 900 MHz FSK and LoRa as its RF layer there is a lot information on how it works. As you might expect they have addressed the privacy and security issues through encryption, minimising the data transmitted, and constantly changing identifiers. To read the Amazon document at face value is to enter a world in which some confidence can be gained in the product.
The question on the lips of skeptical readers will no doubt be this: what could possibly go wrong? We would expect that the devices themselves and the radio portion of the network will be investigated thoroughly by those who make it their business to do such things, and while there is always the chance that somebody could discover a flaw in them it’s more probable that weaknesses could be found in the applications that sit atop the system. It’s something that has plagued Amazon’s IoT offerings before, such as last year when their Neighbors app was found to sit atop a far more garrulous API than expected, leading to a little more neighbourly information being shared than they bargained for. If Amazon’s blurb is to be believed then this system is to be opened up for third-party IoT device and app developers, and with each one of those the possibility of holes waiting to be discovered increases. We’ll keep you posted as they emerge.
Products such as Amazon Echo and Ring are incredible showcases of 21st century technology. They’re the living embodiment of an automated Jetsons future, and we’d be lying if we said we didn’t want a little slice of that future. But as you all know, the version of that future peddled by them and their competitors is a deeply flawed one in which the consumers who buy the products are largely unaware of how much data is created from them. From a purely technical perspective the idea of home security products that automatically form a low bandwidth network for use in case of main network failure is an exceptionally cool one, but when coupled with the monster data slurp of the Amazon behemoth it assumes a slightly more worrying set of possibilities. Is it possible to be George Jetson without Mr. Spacely gazing over your shoulder?
It’s probably a dream most of us share, to stumble upon a dusty hall full of fascinating abandoned tech frozen in time as though its operators walked away one day and simply never returned. It’s something documented by some Russian urban explorers who found an unremarkable office building with one of its floors frozen sometime around the transition from Soviet Union to Russian Federation. In it they found their abandoned tech, in the form of a cross-section of Soviet-era computers form the 1970s onwards.
As you might expect, in a manner it mirrors the development of civilian computing on the capitalist side of the Iron Curtain over a similar period, starting with minicomputers the size of several large refrigerators and ending with desktop microcomputers. The minis seem to all be Soviet clones of contemporary DEC machines. with some parts of them even looking vaguely familiar. The oldest is a Saratov-2, a PDP/8 clone which we’re told is rare enough for no examples to have been believed to have survived until this discovery. We then see a succession of PDP/11 clones each of which becomes ever smaller with advancements in semiconductor integration, starting with the fridge-sized units and eventually ending up with desktop versions that resemble 1980s PCs.
While mass-market Western desktop machines followed the path of adopting newer architectures such as the Z80 or the 8086 the Soviets instead took their minicomputer technology to that level. It would be interesting to speculate how these machines might further have developed over the 1990s had history been different. Meanwhile we all have a tangible legacy of Soviet PDP/11 microcomputers in the form of Tetris, which was first written on an Elektronika 60.
We know that among our readers there is likely to be a few who encountered similar machines in their heyday, and we hope they’ll share their recollections in the comments. Meanwhile we hope that somehow this collection can be preserved one day. If your thirst for dusty mincomputers knows no bounds, read about the collectors who bought an IBM machine on eBay and got more than they bargained for.
A fact universally known among the Hackaday community is that projects are never truly done. You can always spin another board release to fix a silkscreen mistake, get that extra little boost of performance, or finally spend the time to track down that weird transient bug. Or in [ultraembedded’s] case, take a custom FPGA player from 800 x 600 to 1280 x 720. The hardware used is a Digilent Arty A7 and PMOD boards for I2S2, VGA, and MicroSD. We previously covered this project back when it was first getting started.
Getting from 800 x 600 to 1280 x 720 — 31% more pixels — required implementing a higher performance JPEG decoder that can read in the MPJEG frames, pushing out a pixel every 2.1 clock cycles. The improvements also include a few convenience features such as an IR remote. The number of submodules inside the system is just incredible, with most of them being implemented or tweaked by [ultraembedded] himself.
For the FPGA Verilog, there’s the SD/MMC interface, the JPEG decoder, the audio controller, the DVI framebuffer, a peripheral core, and a custom RISC-V CPU. For the firmware loaded off the SD card, it uses a custom RTOS running an MP3 decoder, a FAT32 interface, an IR decoder, and a UI based on LVGL.
We think this project represents a wonderful culmination of all the different IP cores that [ultraembedded] has produced over the years. All the code for the FPGA media player is available on GitHub.
I think I’ve built myself an HD (720p50) video player out of an #FPGA, #RISCV, #MJPEG and 27,000 lines of Verilog! Going from 800×600 -> 1280×720 just worked with 10 more MHz! I actually plan to sit down and watch a movie on this one evening! https://t.co/4G1ZiN2ipY
Useless machines are generally built as a fun pastime, as they do nothing of value by their very definition. The most popular type generally involves a self-cancelling switch. However, there’s plenty of other useless machines to build, and we think [Jeffery’s] build is particularly creative.
The build consists of an XY gantry that moves a standard computer mouse. To control the gantry, a Raspberry Pi feeds the system G-Code relative to the motion of a second mouse plugged into the single-board computer. It’s pretty standard fare overall, with the Pi sending commands to an Arduino that runs the various stepper motors via a CNC controller shield.
Yes, it’s a mouse that moves a mouse – and on the surface, this appears to be a very useless machine. However, we could imagine it being useful for remote control of a very old system that uses a non-standard mouse that is otherwise difficult to emulate. Additionally, it wouldn’t take much extra work to turn the XY gantry into a competent pen-plotter – of which we’ve seen many. Video after the break.
The device uses an ESP32 to connect to WiFi, and then query Google Apps for a given user’s calendar details on a daily basis. After grabbing the data, it’s fed out to a thermal printer connected over serial at 9600 baud. As a twist, [lokthelok] has produced two versions of firmware for the project. The master version simply scrapes calendar data and outputs it neatly. The Useless version goes further, jumbling up appointments and printing them out of order. If you’ve got nothing on for the day, it will instead spool out the remainder of the thermal paper on the roll.
While concerns over COVID-19 probably kept many a guest room empty this Thanksgiving, things were a little different aboard the International Space Station. The four-seat SpaceX Crew Dragon is able to carry one more occupant to the orbiting outpost than the Russian Soyuz, which has lead to a somewhat awkward sleeping arrangement: there are currently seven people aboard a Station that only has six crew cabins. To remedy the situation, Commander Michael Hopkins has decided to sleep inside the Crew Dragon itself, technically giving himself the most spacious personal accommodations on the Station. This might seem a little hokey, but it’s actually not without precedent; when the Shuttle used to dock with the ISS, the Commander would customarily sleep in the cockpit so they would be ready to handle any potential emergency.
Speaking of off-world visitation, the Hayabusa2 spacecraft is nearly home after six years in space. It won’t be staying long though, the deep-space probe is only in the neighborhood to drop off a sample of material collected from the asteroid Ryugu. If all goes according to plan, the small capsule carrying the samples will renter the atmosphere and land in the South Australian desert on December 6th, while Hayabusa2 heads back into the black for an extended mission that would have it chasing down new asteroids into the 2030s.
Moving on to a story that almost certainly didn’t come from space, a crew from the Utah Division of Wildlife Resources recently discovered a strange metal monolith hidden in the desert. While authorities were careful not to disclose the exact coordinates of the object, it didn’t take Internet sleuths long to determine its location, in part thanks to radar data that allowed them to plot the flight path of a government helicopters. Up close inspections that popped up on social media revealed that the object seemed to be hollow, was held together with rivets, and was likely made of aluminum. It’s almost certainly a guerrilla art piece, though there are also theories that it could have been a movie or TV prop (several productions are known to have filmed nearby) or even some kind of military IR/radar target. We may never know for sure though, as the object disappeared soon after.
Even if you’re not a fan of Apple, it’s hard not to be interested in the company’s new M1 chip. Hackers have been clamoring for more ARM laptops and desktops for years, and with such a major player getting in the game, it’s only a matter of time before we start seeing less luxurious brands taking the idea seriously. After the recent discovery that the ARM version of Ubuntu can run on the new M1 Macs with a simple virtualization layer, it looks like we won’t have to wait too long before folks start chipping away at the Walled Garden.
In the market for a three phase servo controller? A reader who’s working on a robotics project worth as much as a nice house recently wrote in to tell us about an imported driver that goes for just $35. Technically it’s designed for driving stepper motors, but it can also (somewhat inefficiently) run servos. Our informant tells us that you’d pay at least $2,000 for a similar servo driver from Allen-Bradley, so the price difference certainly seems to make up for the hit in performance.
Finally, some bittersweet news as we’ve recently learned that Universal Radio is closing. After nearly 40 years, proprietors Fred and Barbara Osterman have decided it’s time to start winding things down. The physical store in Worthington, Ohio will be shuttered on Monday, but the online site will remain up for awhile longer to sell off the remaining stock. The Ostermans have generously supported many radio clubs and organizations over the years, and they’ll certainly be missed. Still, it’s a well-deserved retirement and the community wishes them the best.
One of the more interesting display technologies of the moment comes from Sharp, their memory display devices share the low power advantages of an e-ink display with the much faster updates we would expect from an LCD or similar. We’ve not seen much of them in our community due to cost, so it’s good to see one used in an MQTT dashboard project from [Raphael Baron].
The hardware puts the display at the top of a relatively minimalist 3D printed encloseure with the LOLIN32 ESP32 development board behind it, and with a plinth containing a small rotary encoder and three clicky key switches in front. The most interesting part of the project is surprisingly not the display though, because despite being based upon an ESP32 development board he’s written its software with the aim of being as platform- and display-independent as possible. To demonstrate this he’s produced it as a desktop application as well as the standalone hardware. A simple graphical user interface allows the selection of a range of available sources to monitor, with the graphical results on the right.
All code and other assets for the project can be found in a handy GitHub repository, and to put the thing through its paces he’s even provided a video that we’ve placed below the break. User interfaces for MQTT-connected devices can talk as well as listen, for example this MQTT remote control.
Every time manufacturers bring a new “unpickable” lock to market, amateur and professional locksmiths descend on the new product to prove them wrong. [Shane] from [Stuff Made Here] decided to try his hand at designing and building an unpickable lock, and found that particular rabbit hole to be a lot deeper than expected. (Video, embedded below.)
Most common pin tumbler locks can be picked thanks to slightly loose fits of the pins and tiny manufacturing defects. By lifting or bumping the pins while putting tension on the cylinder the pins can be made to bind one by one at the shear line. Once all the pins are bound in the correct position, it can be unlocked.
[Shane]’s design aimed to prevent the pins from being set in unlocked position one by one, by locking the all pins in whatever position they are set and preventing further manipulation when the cylinder is turned to test the combination. In theory this should prevent the person doing the picking from knowing if any of the pins were in the correct position, forcing them to take the difficult and time-consuming approach of simply trying different combinations.
[Shane] is no stranger to challenging projects, and this one was no different. Many of the parts had to be remade multiple times, even with his well-equipped home machine shop. The mechanism that holds the pins in the set position when the cylinder is rotated was especially difficult to get working reliably. He explicitly states that this lock is purely an educational exercise, and not commercially viable due to its mechanical complexity and difficult machining.
A local locksmith was unsuccessful in picking the lock with the standard techniques, but the real test is still to come. The name [LockPickingLawyer] has probably already come to mind for many readers. [Shane] has been in contact with him and will send him a lock to test after a few more refinements, and we look forward to seeing the results!




 that constantly reads the back EMF to determine the load the motor is under. If you have it flag you right before the motor hits the end of the rail and stalls, bam, you have a firmware limit switch. Watch it remove crusts and chop a lot of carrots with faces after the break.
