Local And Remote Debugging With GDB

As a debugger, GDB is a veritable Swiss Army knife. And just like exploring all of the non-obvious uses of a those knives, your initial response to the scope of GDB’s feature set is likely to be one of bewilderment, subsequent confusion, and occasional laughter. This is an understandable reaction in the case of the Swiss Army knife as one is unlikely to be in the midst of an army campaign or trapped in the wilderness. Similarly, it takes a tricky debugging session to really learn to appreciate GDB’s feature set.

If you have already used GDB to debug some code, it was likely wrapped in the comfort blanket of an IDE. This is of course one way to use GDB, but limits the available features to what the IDE exposes. Fortunately, the command line interface (CLI) of GDB has no such limitations. Learning the CLI GDB commands also has the advantage that one can perform that critical remote debug session even in the field via an SSH session over the 9600 baud satellite modem inside your Swiss Army knife, Cyber Edition.

Have I carried this analogy too far? Probably. But learning the full potential of GDB is well worth your time so today, let’s dive in to sharpen our digital toolsets.

Godmode for Running Code
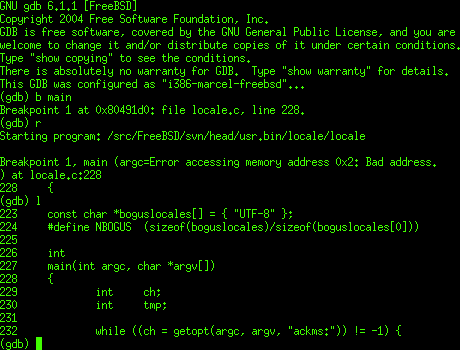
Example GDB session.

The concept behind a debugger is fairly uncomplicated: all too often something is preventing code which you have written from working, or you want to take a closer look at certain states within the application as it is executing. A simple way to do this is by printing out the values of variables to a terminal or serial port, but the much more powerful way is to use a debugger like GDB to interactively work with the code as it executes.

This means pausing the execution, stepping forward and backward through individual lines of code, inspecting stack frames and parts of memory, modifying the contents of memory and specific variables, and so on. Along with the setting of breakpoints and the watching of variables, virtually any part of the application’s execution can be monitored and influenced. This includes when things go south and the execution terminates with some fault condition, allowing a stack trace to be recalled.

While GDB can be used with any application’s binary, it’s infinitely more useful when the debug symbols are also provided to the debugger. These debug symbols are text strings including source code, as well as other information. They are included in the binary by the compiler when instructed to do so. For GCC-based compilers and LLVM this is usually done using the -g flag.

Local Hero

Running through a local debug session is a good way to become acquainted with how to use GDB’s command line interface. Be sure to have a handy command reference within easy reach at any time when using GDB. Doing so will make it easy to become familiar with the more involved commands.

The essential ones to know are break (b), for setting a break point, info for obtaining information locals, threads, etc. Further backtrace (bt) and continue (c), next (n) and step (s) for printing out a backtrace, continuing execution and moving through the code in increments, respectively. After loading the executable with GDB, the program is started with run (r), which can be supplied with any command line arguments to the executable.

Let’s write a very simple program we can use for debugging practice:

/* hello.c - Hello World */

#include<stdio.h>

int main(void) {
        char hello[] = "Hello World";
        printf("%s\n", hello);
        return 0;
}

We’ll use the -g3 flag when compiling to include debug symbols. Now let’s walk through this C-based Hello World example:

gcc -o hello -g3 hello.c
gdb ./hello

[..]
(gdb) b main
Breakpoint 1 at 0x1169: file hello.c, line 5.
(gdb) run
Starting program: /home/hackaday/hello
Breakpoint 1, main() at hello.c:5
5 int main(void) {
(gdb) n
6 char hello[] = "Hello World";
(gdb) n
7 printf("%s\n", hello);
(gdb)

We first set a break point at the main()function, then run to start the program. After the breakpoint, with each execution of next (or just hitting enter on an empty input to repeat the previous command), we’ll proceed to the next line of the application, without stepping into function calls. That’s what step is for. If we use printf() in the code, for example, using step would cause us to examine every line of that function and its implementation as well. Whether this is desirable depends on one’s needs.

Finally, we can examine variables and memory using print (p) for printing variables and x to print bytes at a memory address. E.g.:

(gdb) print hello
$1 = "Hello World"

Most of the commands are quite straight-forward, and safe. Barring the use of GDB’s set command, using which one can not only change GDB’s settings, but also edit memory contents. Use this one with caution.

Jacking Into the Remote

Running a remote GDB session is roughly the same as a local session, with the obvious complication of having to establish the session on a remote system. Said remote system can be anything from a server, desktop or other system running a full-blown OS, down to a microcontroller (MCU) running straight on the bare metal.

The main requirement for GDB to establish a debugging session on a remote system, is for there to be a GDB server (gdbserver) instance which the GDB tool can connect to. This GDB server then acts as a bridge between GDB and the active debug session. This connection can be established via TCP or a serial line. This makes it a highly portable approach that works both for remote servers or desktop systems, as well as industrial boards with an RS-232C link.

Even more interesting is to use the GDB server approach to create a bridge to the in-circuit debugger functionality provided by microcontroller platforms such as ST’s STM32 Cortex-M-based systems. This same approach will work with few modifications for Microchip’s ARM-based SAM and AVR platforms.

OpenOCD as GDB server

Anyone who has done MCU development is likely familiar with OpenOCD. This tool is invaluable in the programming of a wide variety of MCUs, but also comes with a built-in GDB server. As an example, imagine wanting to establish a GDB session on an STM32 MCU, on a common development board like the STM32F4-Discovery one.

The first step is to start OpenOCD’s GDB server:

openocd -f board/stm32f4discovery.cfg

Next, we can connect to this server via the loopback interface, while also providing GDB (from the arm-none-eabi toolchain) with the path to the ELF binary containing the firmware:

arm-none-eabi-gdb --eval-command="target remote localhost:3333" "hello_world.elf"

GDB will now connect to the GDB server, with OpenOCD using the STM32F4-Discovery board’s in-circuit debugger feature of the onboard ST-Link/V2 interface. All protocol translation is now done by OpenOCD, enabling all the usual GDB features, even though the code we are debugging runs on the MCU on the development board.

As the MCU will already have booted the firmware we wish to debug, we will still have to perform one more step, which is to reset the MCU to get a GDB session we can use:

(gdb) mon reset halt

The MCU will now have been reset and in a halted state until we do something. We will now add a new temporary breakpoint and continue:

(gdb) tbreak main
(gdb) c

After continuing execution, this temporary breakpoint puts us right at the beginning of our main function, from which we can set up breakpoints and more as needed. For example, we can check out the value of a specific register of the GPIOA peripheral on this STM32F4-based board. Say we want to see whether the input and output states were set properly in the GPIO_MODER register:

(gdb) x/4tb 0x40020000
$1 = 0100 0000 0000 0000

The special syntax of the x command prints a single 32-bit address, as blocks of single bytes. The GPIOA peripheral location is found in the STM32F407 datasheet, with the Reference Manual (RM) listing the offsets for specific registers within the memory-mapped IO for that peripheral type. In this case the MODER register is at offset 0x00, with GPIOA at address 0x40020000. The byte order is printed left to right, meaning that the first byte is on the left side.

In this case we can see that MODER1 (for pin 1) is set to ’01’, meaning general-purpose output mode.

Time to Quit Guessing

Many are the times when I found myself or others get stuck pouring over lines of code, speculating which one of those lines might be the cause of the weird symptoms. Suffice it to say that doing so is neither fun nor productive. Along with tools like Valgrind, debuggers like GDB are perfect for getting answers to questions, even questions you didn’t know you wanted to ask. It’s especially useful with something like embedded development, where the immediate feedback from newly flashed firmware might be… absent or not quite as expected.

It pays to establish a strict routine of testing for isolating test cases, and to hit the problematic firmware in-situ with a targeted testing plan, using tools like GDB. Create a checklist of which items to check first when something doesn’t work, then work your way up from there.

As non-deterministic as debugging sometimes may seem — and with Heisenbugs certainly endeavoring to make it appear that way — in the end there’s a good, solid reason for every issue. You just need to find out what bit to look at in which manner. Becoming comfortable with a powerful tool like GDB is definitely a major asset there.

source https://hackaday.com/2020/11/06/local-and-remote-debugging-with-gdb/

Local And Remote Debugging With GDB

As a debugger, GDB is a veritable Swiss Army knife. And just like exploring all of the non-obvious uses of a those knives, your initial response to the scope of GDB’s feature set is likely to be one of bewilderment, subsequent confusion, and occasional laughter. This is an understandable reaction in the case of the Swiss Army knife as one is unlikely to be in the midst of an army campaign or trapped in the wilderness. Similarly, it takes a tricky debugging session to really learn to appreciate GDB’s feature set.

If you have already used GDB to debug some code, it was likely wrapped in the comfort blanket of an IDE. This is of course one way to use GDB, but limits the available features to what the IDE exposes. Fortunately, the command line interface (CLI) of GDB has no such limitations. Learning the CLI GDB commands also has the advantage that one can perform that critical remote debug session even in the field via an SSH session over the 9600 baud satellite modem inside your Swiss Army knife, Cyber Edition.

Have I carried this analogy too far? Probably. But learning the full potential of GDB is well worth your time so today, let’s dive in to sharpen our digital toolsets.

Godmode for Running Code

Example GDB session.

The concept behind a debugger is fairly uncomplicated: all too often something is preventing code which you have written from working, or you want to take a closer look at certain states within the application as it is executing. A simple way to do this is by printing out the values of variables to a terminal or serial port, but the much more powerful way is to use a debugger like GDB to interactively work with the code as it executes.

This means pausing the execution, stepping forward and backward through individual lines of code, inspecting stack frames and parts of memory, modifying the contents of memory and specific variables, and so on. Along with the setting of breakpoints and the watching of variables, virtually any part of the application’s execution can be monitored and influenced. This includes when things go south and the execution terminates with some fault condition, allowing a stack trace to be recalled.

While GDB can be used with any application’s binary, it’s infinitely more useful when the debug symbols are also provided to the debugger. These debug symbols are text strings including source code, as well as other information. They are included in the binary by the compiler when instructed to do so. For GCC-based compilers and LLVM this is usually done using the -g flag.

Local Hero

Running through a local debug session is a good way to become acquainted with how to use GDB’s command line interface. Be sure to have a handy command reference within easy reach at any time when using GDB. Doing so will make it easy to become familiar with the more involved commands.

The essential ones to know are break (b), for setting a break point, info for obtaining information locals, threads, etc. Further backtrace (bt) and continue (c), next (n) and step (s) for printing out a backtrace, continuing execution and moving through the code in increments, respectively. After loading the executable with GDB, the program is started with run (r), which can be supplied with any command line arguments to the executable.

Let’s write a very simple program we can use for debugging practice:

/* hello.c - Hello World */

#include<stdio.h>

int main(void) {
        char hello[] = "Hello World";
        printf("%s\n", hello);
        return 0;
}

We’ll use the -g3 flag when compiling to include debug symbols. Now let’s walk through this C-based Hello World example:

gcc -o hello -g3 hello.c
gdb ./hello

[..]
(gdb) b main
Breakpoint 1 at 0x1169: file hello.c, line 5.
(gdb) run
Starting program: /home/hackaday/hello
Breakpoint 1, main() at hello.c:5
5 int main(void) {
(gdb) n
6 char hello[] = "Hello World";
(gdb) n
7 printf("%s\n", hello);
(gdb)

We first set a break point at the main()function, then run to start the program. After the breakpoint, with each execution of next (or just hitting enter on an empty input to repeat the previous command), we’ll proceed to the next line of the application, without stepping into function calls. That’s what step is for. If we use printf() in the code, for example, using step would cause us to examine every line of that function and its implementation as well. Whether this is desirable depends on one’s needs.

Finally, we can examine variables and memory using print (p) for printing variables and x to print bytes at a memory address. E.g.:

(gdb) print hello
$1 = "Hello World"

Most of the commands are quite straight-forward, and safe. Barring the use of GDB’s set command, using which one can not only change GDB’s settings, but also edit memory contents. Use this one with caution.

Jacking Into the Remote

Running a remote GDB session is roughly the same as a local session, with the obvious complication of having to establish the session on a remote system. Said remote system can be anything from a server, desktop or other system running a full-blown OS, down to a microcontroller (MCU) running straight on the bare metal.

The main requirement for GDB to establish a debugging session on a remote system, is for there to be a GDB server (gdbserver) instance which the GDB tool can connect to. This GDB server then acts as a bridge between GDB and the active debug session. This connection can be established via TCP or a serial line. This makes it a highly portable approach that works both for remote servers or desktop systems, as well as industrial boards with an RS-232C link.

Even more interesting is to use the GDB server approach to create a bridge to the in-circuit debugger functionality provided by microcontroller platforms such as ST’s STM32 Cortex-M-based systems. This same approach will work with few modifications for Microchip’s ARM-based SAM and AVR platforms.

OpenOCD as GDB server

Anyone who has done MCU development is likely familiar with OpenOCD. This tool is invaluable in the programming of a wide variety of MCUs, but also comes with a built-in GDB server. As an example, imagine wanting to establish a GDB session on an STM32 MCU, on a common development board like the STM32F4-Discovery one.

The first step is to start OpenOCD’s GDB server:

openocd -f board/stm32f4discovery.cfg

Next, we can connect to this server via the loopback interface, while also providing GDB (from the arm-none-eabi toolchain) with the path to the ELF binary containing the firmware:

arm-none-eabi-gdb --eval-command="target remote localhost:3333" "hello_world.elf"

GDB will now connect to the GDB server, with OpenOCD using the STM32F4-Discovery board’s in-circuit debugger feature of the onboard ST-Link/V2 interface. All protocol translation is now done by OpenOCD, enabling all the usual GDB features, even though the code we are debugging runs on the MCU on the development board.

As the MCU will already have booted the firmware we wish to debug, we will still have to perform one more step, which is to reset the MCU to get a GDB session we can use:

(gdb) mon reset halt

The MCU will now have been reset and in a halted state until we do something. We will now add a new temporary breakpoint and continue:

(gdb) tbreak main
(gdb) c

After continuing execution, this temporary breakpoint puts us right at the beginning of our main function, from which we can set up breakpoints and more as needed. For example, we can check out the value of a specific register of the GPIOA peripheral on this STM32F4-based board. Say we want to see whether the input and output states were set properly in the GPIO_MODER register:

(gdb) x/4tb 0x40020000
$1 = 0100 0000 0000 0000

The special syntax of the x command prints a single 32-bit address, as blocks of single bytes. The GPIOA peripheral location is found in the STM32F407 datasheet, with the Reference Manual (RM) listing the offsets for specific registers within the memory-mapped IO for that peripheral type. In this case the MODER register is at offset 0x00, with GPIOA at address 0x40020000. The byte order is printed left to right, meaning that the first byte is on the left side.

In this case we can see that MODER1 (for pin 1) is set to ’01’, meaning general-purpose output mode.

Time to Quit Guessing

Many are the times when I found myself or others get stuck pouring over lines of code, speculating which one of those lines might be the cause of the weird symptoms. Suffice it to say that doing so is neither fun nor productive. Along with tools like Valgrind, debuggers like GDB are perfect for getting answers to questions, even questions you didn’t know you wanted to ask. It’s especially useful with something like embedded development, where the immediate feedback from newly flashed firmware might be… absent or not quite as expected.

It pays to establish a strict routine of testing for isolating test cases, and to hit the problematic firmware in-situ with a targeted testing plan, using tools like GDB. Create a checklist of which items to check first when something doesn’t work, then work your way up from there.

As non-deterministic as debugging sometimes may seem — and with Heisenbugs certainly endeavoring to make it appear that way — in the end there’s a good, solid reason for every issue. You just need to find out what bit to look at in which manner. Becoming comfortable with a powerful tool like GDB is definitely a major asset there.

source https://hackaday.com/2020/11/06/local-and-remote-debugging-with-gdb/

Hackaday Podcast 092: Orbital Data by Mail, Human Flight on Styrofoam Wings, and Seven Shades of E-Ink

Hackaday editors Elliot Williams and Mike Szczys catch the best hacks you may have missed. This week we look at the new Raspberry Pi 400, use computer vision to get ready for geeky Christmas, and decypher a negative-space calendar. We get an answer to the question of what happens if you scale up a styrofoam airplane to human-size. Facebook is locking down VR headset, will hackers break them free? And take an excellent stroll down memory lane to find out what it was like to be a space-obsessed ham at the dawn of personal computers.

Take a look at the links below if you want to follow along, and as always, tell us what you think about this episode in the comments!

Direct download (~60 MB)

Places to follow Hackaday podcasts:

Episode 092 Show Notes:

New This Week:

Interesting Hacks of the Week:

Quick Hacks:

Can’t-Miss Articles:

source https://hackaday.com/2020/11/06/hackaday-podcast-092-orbital-data-by-mail-human-flight-on-styrofoam-wings-and-seven-shades-of-e-ink/

Robots Learning to Understand Their Surroundings

Today it is pretty easy to build a robot with an onboard camera and have fun manually driving through that first-person view. But builders with dreams of autonomy quickly learn there is a lot of work between camera installation and autonomously executing a “go to chair” command. Fortunately we can draw upon work such as View Parsing Network by [Bowen Pan, Jiankai Sun, et al]

When a camera image comes into a computer, it is merely a large array of numbers representing red, green, and blue color values and our robot has no idea what that image represents. Over the past years, computer vision researchers have found pretty good solutions for problems of image classification (“is there a chair?”) and segmentation (“which pixels correspond to the chair?”) While useful for building an online image search engine, this is not quite enough for robot navigation.

A robot needs to translate those pixel coordinates into real-world layout, and this is the problem View Parsing Network offers to solve. Detailed in Cross-view Semantic Segmentation for Sensing Surroundings (DOI 10.1109/LRA.2020.3004325) the system takes in multiple camera views looking all around the robot. Results of image segmentation are then synthesized into a 2D top-down segmented map of the robot’s surroundings. (“Where is the chair located?”)

The authors documented how to train a view parsing network in a virtual environment, and described the procedure to transfer a trained network to run on a physical robot. Today this process demands a significantly higher skill level than “download Arduino sketch” but we hope such modules will become more plug-and-play in the future for better and smarter robots.

[IROS 2020 Presentation video (duration 10:51) requires free registration, available until at least Nov. 25th 2020. One-minute summary embedded below.]

source https://hackaday.com/2020/11/06/robots-learning-to-understand-their-surroundings/

Today at Remoticon: Bring-a-Hack

Last Chance Tickets:

General admission tickets for this weekend’s Hackaday Remoticon are only available for two more hours! These are free, but you need to have one to get in on tonight’s Bring-a-hack.

Today’s Live Events:

The Community Bring-a-Hack meetup for all general admission ticket holders begins today at 16:00 PST. Check the ticketing hub page for your link to the event which is being held on Remo.

Live streaming events open to the public will begin on Saturday at 10:00 PST with open remarks and Kipp Bradford’s keynote talk. Workshops and the SMD Challenge will live-stream all day. And Alfred Jones will present his keynote at 18:30 PST followed by the Hackaday Prize Ceremony. Follow our media channels to be notified of all live streams:

source https://hackaday.com/2020/11/06/today-at-remoticon-bring-a-hack/

This Week in Security: In the Wild, Through Your NAT, and Brave

Most of the stories from this week are vulnerabilities dropped before fixes are available, many of them actively being exploited. Strap yourselves in!

Windows Kernel Crypto

The first is CVE-2020-17087, an issue in the Windows Kernel Cryptography Driver. The vulnerable system calls are accessible from unprivileged user-space, and potentially even from inside sandboxed environments. The resulting buffer overflow can result in arbitrary code executing in the kernel context, meaning this is a quick jump to root-level control over a victim system.

What exactly is the code flaw here that’s being attacked? It’s in a bit of buffer allocation logic, inside a binary-to-hex conversion routine. The function accepts an unsigned short length argument. That value is used to calculate the output buffer size, by multiplying it by six, and using an unsigned short to hold that value. See the problem? A sufficiently large value will roll over, and the output buffer size will be too small. It’s a value overflow that leads to a buffer overflow.

Because the problem is being actively exploited, the report has been made public just seven days after discovery. The flaw is still unpatched in Windows 10, as of the time of writing. It also seems to be present as far back as Windows 7, which will likely not receive a fix, being out of support. [Editor’s snarky note: Thanks, closed-source software.]

Intel Key Extraction

Microcode has been a part of CPU architecture for decades. From a certain point of view, processors have always had some sort of microcode — logic that converts instructions into discrete hardware operations. Microcode, as we think of it today, came to x86 processors with the Pentium Pro. With that processor, it was finally possible to update the microcode layer at boot, fixing bugs and problems that were found after manufacture. Intel has always distributed that microcode as an encrypted blob, keeping researchers from investigating the changes between updates. That restriction may be lifted, as a trio of researchers have managed to extract the encryption key from modern Intel CPUs.

The extraction is possible because of a vulnerability allowing access to a debug interface inside Intel chips. This technique requires physical access to the machine, and the chip resets to its factory state on a power cycle. Time will tell what other interesting tidbits will be mined from the hidden depths of Intel processors. Keep an eye on the Chip Red Pill repository for their ongoing work.

Oracle In the Wild

Two separate attacks are being actively used against Oracle products. The first is CVE-2020-14882 in Weblogic, a pre-auth RCE that just requires a single HTTP GET to trigger. This was patched in the latest set of security updates, and quickly reverse engineered. (That’s written in Vietnamese. Google translate does well enough to follow along.)

The second attack is CVE-2020-14871, a PAM vulnerability in Oracle’s Solaris. This was a true zero-day, being exploited for months before it was fixed in the same set of security updates. FireEye was the company that originally found the attack, and have been kind enough to explain it. The Pluggable Authentication Module (PAM) has a maximum response size, and uses that size to construct a buffer to hold incoming requests. The Solaris code fails to do any checks on the request, and just naively copies the string into the buffer, right past the end, if the input string is too long.

Now where do you think we could manipulate the input message for a PAM request? How about the Secure SHell Daemon? Yep, make an SSH request in keyboard-interactive mode, and use a username longer than 512 characters. In a simple test, PAM just crashes, but it’s possible to manipulate the username to compromise the machine instead.

This is a worst-case scenario. The default configuration of Solaris’ SSHD daemon was vulnerable to a simple compromise. All it takes is SSH exposed to the internet, and your machine probably got compromised. It does appear that using an SSH key, and disabling all the other SSH login methods would mitigate this vulnerability, particularly if you go so far as disabling SSH PAM altogether. This vulnerability is also present in OpenIndiana as well. 2020.10 should contain the fixes, but I can’t find any information about the previous release, 2020.04 being patched. Caveat Emptor.

Beware The BMC

I’ve always looked upon Baseboard Management Controllers (BMCs) with great skepticism. Yes, it’s incredibly useful to have a way to access a remote computer’s BIOS interface. A BMC can even be used to do a remote reinstall of the entire OS. For a machine locked away in a remote datacenter, a BMC can be a life-saver.

That BMC is also a second OS running on your hardware, that you don’t control. I’ve never been comfortable connecting that black-box OS to the internet. I have a pair of servers, and I used a secondary Ethernet port on each server to cross-connect from each server into the other’s BMC port. I can SSH in and access the interface, while keeping the BMCs completely isolated. It turns out, my paranoia is entirely justified. This article is specific to an NVIDIA SCADA system, but at least some of these vulnerabilities are present in other iterations of this BMC system. The worst offender is CVE‑2020‑11483, hardcoded credentials. This sort of bug is usually a debugging account that someone forgot to disable before shipping the firmware, it still represents a major backdoor into any system running this BMC. The old adage is still relevant: Don’t connect it to the internet!

Google’s Project Zero Details GitHub Vulnerability

Project Zero has published the details of a flaw in GitHub’s Actions system. You’ve probably interacted with Actions — when a project automatically runs a test suite on pull requests, or copies new bug reports to other repositories, it’s Actions under the hood. The vulnerability is command injection. The Project Zero bug report points out the set-env command as the most troubling, and since their PoC includes arguments being sent to the underlying Node server, I’m inclined to agree.

The political angle here is interesting too. GitHub asked for a disclosure extension at the 11th hour, 103 days after receiving the report. In their defense on October 1st, GitHub did publish an advisory disclosing essentially everything but PoC code. This just happens to be one of those security problems that happens to also be a feature for some users. If you manage a GitHub project that uses Actions, it’s probably worth taking some time to make sure you aren’t vulnerable to command injection.

Slipstreaming Through NAT

NAT, love it or hate it, has been part of our networks for years now. Regardless of whether it’s really a firewall or not, I agree with Robert Graham’s opinion:

To shake things up a bit, enter Slipstream, a very clever attack against NAT routers that support connection tracking. You may have seen this in iptables, in the RELATED keyword. SIP is a notable example of why connection tracking is useful. You pick up the phone on your desk, and dial a number. That phone opens a SIP control connection, and issues INVITEs to set up the conversation with your SIP provider. The INVITE information includes the details on the actual audio connection. Usually this is shuffled off to a high level UDP port. A headache-inducing problem for SIP providers is that NAT will block those audio connections. The solution is to include a conntrack module in the firewall that can read those INVITE messages and correctly forward the audio traffic.

This is the mechanism that Slipstream abuses. Your browser cannot generate a SIP INVITE packet, but it can send HTTP GET messages to 5060, the normal SIP port. Is there a way an attacker could generate HTTP traffic that would confuse the CONNTRACK module? The answer is yes, but it’s difficult.

To effectively fool the NAT router, Slipstream gathers data on the given network, and generates large packets that will fragment in transit. By padding the front of those packets, and aligning the fragmentation point at the start of the spoofed SIP data, a malicious site can indeed fool many NAT routers on the market today. The result is that by connecting to a malicious server, and running the JavaScript hosted there, the machine running the browser is exposed to the attacking server, as if it was no longer behind the NAT router at all. All-in-all it’s a very clever technique, but time will tell whether it ever gets used for attacks in the wild. For now, it’s just a reminder that defense-in-depth is the way to go.

source https://hackaday.com/2020/11/06/this-week-in-security-in-the-wild-through-your-nat-and-brave/

Lunar Ark Boldly Goes

[Sebastian and Karl-Johan] are two award-winning Danish Space Architects who are subjecting themselves to harsh, seemingly uninhabitable conditions, for science. The pair set out to build a lunar base that could land with the manned Moon missions in 2024. Like any good engineering problem, what good is a solution without testing? So the pair have placed their habitat in a Moon Analogue habitat and are staying in their habitat for two months. They want to really feel the remoteness, the bitter cold, and the fatigue of actually being on the moon. So far they are about halfway through their journey and expect to return home in December 2020.

When asking themselves where on Earth is it most like the Moon, they came up with Moriusaq, Greenland. It’s cold, remote, in constant sunlight this time of year, and it is a vast white monochrome landscape just like the moon. The first moon settlement missions are expected to be at the South Pole of the Moon, as known as the Peak of Eternal Light.
The habitat itself is a testament to the duo’s ingenuity. The whole structure folds to fit the tight space and weight requirements of rockets. Taking 2.9m3 (102 ft3) when stored, it expands 560% in volume to 17.2m3 (607 ft3). In Greenland, the structure needs to withstand -30ºC (-22ºF) and 90 km/h winds.
Because the South Pole is in constant sunlight, the temperature varies much less there than on the rest of the Moon, which makes Greenland a very good analogue temperature-wise. The foldable skin is covered in solar panels, both on the top of the bottom. The highly reflective nature of the Moon’s surface makes it easy to capture the light bouncing up onto the bottom of the habitat.

Several other bits of technology have been included onboard, like a 3D printer, a circadian light stimulation system, an algae reactor, and a weather simulation. Since both the Moon and Greenland are in constant sunlight, the pod helps regulate the circadian rhythms of the occupants by changing the hue and brightness throughout the day. The weather simulation tries to break up the monotony of space by introducing weather like a stormy day or rainbow colours.

Their expedition is still ongoing and they post daily mission updates. While some might call their foray into the unknown madness, we call it bold. Currently, NASA is planning its Artemis mission in 2024 and we hope that the lessons learning from the Lunark and other experiments culminate in a better experience for all astronauts.

source https://hackaday.com/2020/11/06/lunar-ark-boldly-goes/

Lunar Ark Boldly Goes

[Sebastian and Karl-Johan] are two award-winning Danish Space Architects who are subjecting themselves to harsh, seemingly uninhabitable conditions, for science. The pair set out to build a lunar base that could land with the manned Moon missions in 2024. Like any good engineering problem, what good is a solution without testing? So the pair have placed their habitat in a Moon Analogue habitat and are staying in their habitat for two months. They want to really feel the remoteness, the bitter cold, and the fatigue of actually being on the moon. So far they are about halfway through their journey and expect to return home in December 2020.

When asking themselves where on Earth is it most like the Moon, they came up with Moriusaq, Greenland. It’s cold, remote, in constant sunlight this time of year, and it is a vast white monochrome landscape just like the moon. The first moon settlement missions are expected to be at the South Pole of the Moon, as known as the Peak of Eternal Light.
The habitat itself is a testament to the duo’s ingenuity. The whole structure folds to fit the tight space and weight requirements of rockets. Taking 2.9m3 (102 ft3) when stored, it expands 560% in volume to 17.2m3 (607 ft3). In Greenland, the structure needs to withstand -30ºC (-22ºF) and 90 km/h winds.

Because the South Pole is in constant sunlight, the temperature varies much less there than on the rest of the Moon, which makes Greenland a very good analogue temperature-wise. The foldable skin is covered in solar panels, both on the top of the bottom. The highly reflective nature of the Moon’s surface makes it easy to capture the light bouncing up onto the bottom of the habitat.

Several other bits of technology have been included onboard, like a 3D printer, a circadian light stimulation system, an algae reactor, and a weather simulation. Since both the Moon and Greenland are in constant sunlight, the pod helps regulate the circadian rhythms of the occupants by changing the hue and brightness throughout the day. The weather simulation tries to break up the monotony of space by introducing weather like a stormy day or rainbow colours.

Their expedition is still ongoing and they post daily mission updates. While some might call their foray into the unknown madness, we call it bold. Currently, NASA is planning its Artemis mission in 2024 and we hope that the lessons learning from the Lunark and other experiments culminate in a better experience for all astronauts.

source https://hackaday.com/2020/11/06/lunar-ark-boldly-goes/

Walmart Gives Up on Stock-Checking Robots

We’ve seen the Jetsons, Star Wars, and Silent Running. In the future, all the menial jobs will be done by robots. But Walmart is reversing plans to have six-foot-tall robots scan store shelves to check stock levels. The robots, from a company called Bossa Nova Robotics, apparently worked well enough and Walmart had promoted the idea in many investor-related events, promising that robot workers would reduce labor costs while better stock levels would increase sales. So why did the retail giant say no to these ‘droids? Apparently, they found better ways to check stock and, according to a quote in the Wall Street Journal’s article about the decision, shoppers reacted negatively to sharing the aisle with the roving machines.

The robots didn’t just check stock. They could also check prices and find misplaced items. You can see a promotional video about the device below.

We have to wonder what this means for robots in general. People like us — Hackaday readers — tend to embrace new technology and we are more likely to follow a robot like this around trying to understand its operation. But we aren’t the majority. Are people afraid for their jobs? Being injured by a runaway machine? A robot uprising?

On the other hand, Walmart continues to use other robots. Notably, I’ve noticed QR-like barcodes that the floor mopper machines use to locate themselves. They also use less mobile robots like cash counters. However, the floor moppers aren’t rolling around during prime shopping hours.

We figure Bossa Nova still has a play. There are plenty of warehouses and maybe even warehouse stores where a machine rolling down an aisle wouldn’t warrant a second look. But if Walmart is afraid to expose customers to the device, we doubt many other retailers will for awhile. Unless there’s something about the demographic. Would people shopping in Home Depot be less worried about a machine? We don’t know.

We also have to wonder what this means for other working robots. We’ve seen robots preparing fast food and driving your car, for example. People are spending a lot of time thinking about how robots will work with coworkers. Maybe they need to also factor in how customers will react to being served by robots or even just sharing space with them.

What do you think? Will it bother you to see a robot taxi drive pass you on the freeway while you eat your robotically-prepared hamburger? Or do you think those who oppose are just modern-day Luddites?

source https://hackaday.com/2020/11/06/walmart-gives-up-on-stock-checking-robots/

A Super UPS for the Pi

One of the problems with using a Raspberry Pi or most other systems in a production environment is dealing with sudden shutdowns due to power loss. Modern operating systems often keep data in memory that should be on disk, and a sudden power cycle can create problems. One answer is an uninterruptible power supply, but maintaining batteries is no fun. [Scott] wanted to do better, so he built a UPS using supercapacitors.

A supercapacitor UPS is nearly ideal. The caps charge quickly and don’t wear out as a battery does. The capacitors also don’t care if they stay in storage for a long time. The only real downside is they don’t have the capacity that batteries can have, but for a small computer like a Pi Zero it is pretty easy to gang up enough capacitors to do the job.

In particular, [Scott’s] design uses five 10F capacitors, each charged to 2.5V. The downside is that this requires a 12V supply, so he did a second design that uses only two capacitors each taking half of a 5V supply.

There are several options for converting the capacitor voltage to the desired output voltage. There’s also software to run the onboard microcontroller and force a shutdown in the Pi if the main power drops.

Naturally, this isn’t an original idea, but it is well done. You can also buy cheap ready-made UPS boards in the Pi form factor, but you might want to check out some aftermarket software for them if you use one.

source https://hackaday.com/2020/11/05/a-super-ups-for-the-pi/

Purdue’s Powerful Paint Could Cancel Climate Change

What if a building could stay cool simply because of its paint job? We’re not talking about putting flames on the sides. Purdue engineers have come up with a formulation of white paint that reflects the heat from sunlight and keeps surfaces cooler than their surroundings. Depending on the location, a building with this paint on the roof may not need air conditioning.

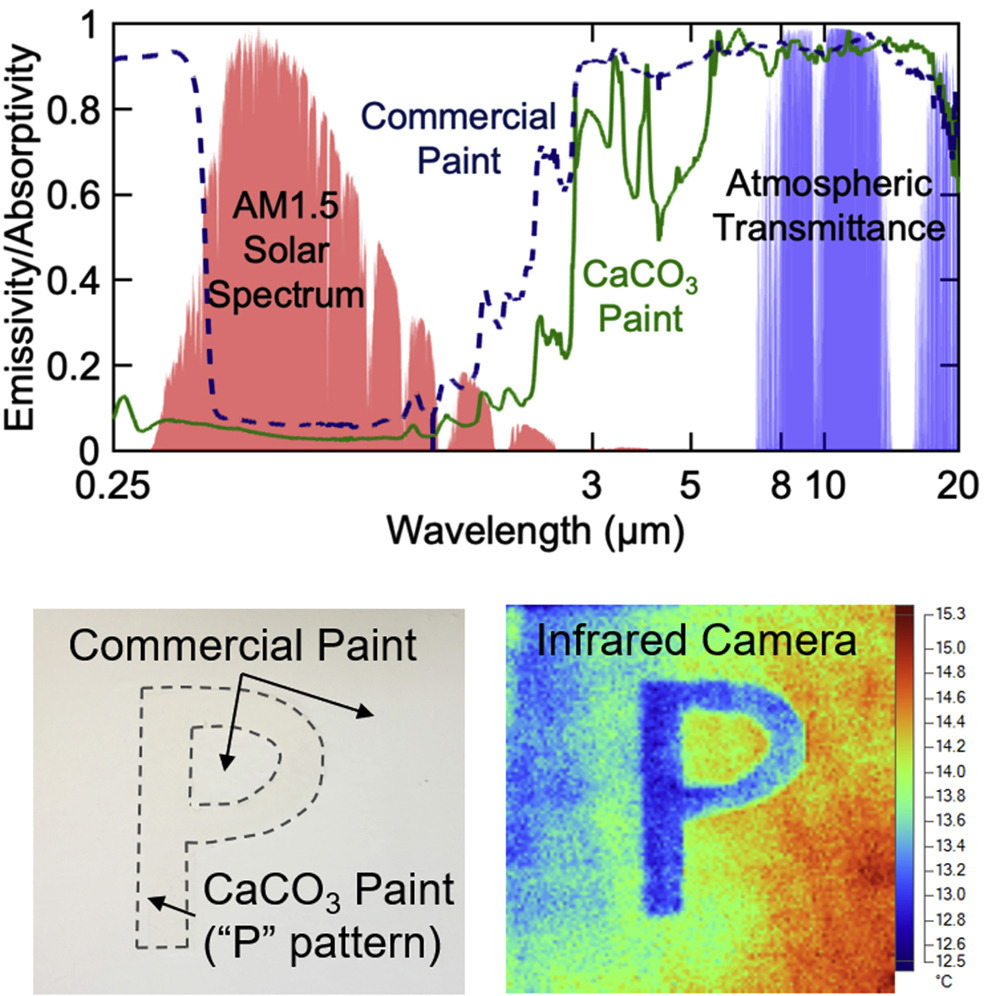
Radiative cooling paint is not a completely new animal, but the formulation developed at Purdue is quite impressive compared to commercially-available paints that only reflect 80-90% of sunlight.

Purdue’s paint reflects 95.5% of sunlight. It can keep surfaces up to 18°F cooler than their surroundings, even in direct sunlight. Where does the heat go? The paint radiates infrared heat, so it escapes the atmosphere and goes into deep space.

How does it do this? With abundantly available calcium carbonate fillers — the chalky stuff that antacids are made of. The paint absorbs next to no UV rays because of the wide band gaps in the atomic structure of calcium carbonate. Take a brief tour of this amazing paint after the break.

We wonder how many rooftops and roadways we’d have to paint with this stuff to have a chance at reversing climate change. It’s not terribly expensive to make, so the problem shifts to widespread education and adoption. What do you think?

source https://hackaday.com/2020/11/05/purdues-powerful-paint-could-cancel-climate-change/

Open Source Lego Controller

A mechanical and manufacturing engineer by day, [Tyler Collins] taught himself electronics and firmware development in his spare time and created an open source Lego controller called Evlōno One. It is based on the STM32 and Arduino ecosystems, and compatible with a impressive variety of existing Lego controllers, sensors and actuators. [Tyler] encountered Lego Mindstorms while helping in an after-school program, and got to wondering whether he could make a more flexible controller. We’d have to say he succeeded, and it’s amazing how much he has packed into this 4 x 4 single-height brick format.

The Evlōno One is based on an ESP32 dual-core MCU, and has WiFi, Bluetooth, and an IR transmitter for wireless connectivity. It also boasts USB-C power delivery, three motor controllers, speakers, LEDs and a button. Dig through the Kickstarted page for more details on these interfaces and specifications. Both the firmware and the hardware will be published as open source on GitHub.

Although [Tyler] has the prototypes all running, he notes this is his first big production effort. FCC certification testing and production mold tooling are the two biggest items driving the scheduled Feb 2021 shipments. If computer driven Lego modeling is one of your hobbies, definitely check out [Tyler]’s project. And if you missed our [Daniel Pikora]’s FOSSCON 2018 presentation about the intersection (collision) of Legos and Open Source, our article must-read for you folks in the Adult Fan of Lego (AFOL) community.

source https://hackaday.com/2020/11/05/open-source-lego-controller/

Giant Blacksmith Vise From Start To Finish

In any proper workshop you want to be able to securely hold a workpiece, whether it’s a tiny PCB or a heavy piece of forged steel. [Jason Marburger] from Fireball Tool needed a really large heavy-duty vise, so he built himself a massive 1490 lbs / 676 kg floor-standing blacksmith vise from scratch.

Blacksmith vises are designed to take a lot of heavy abuse, such as holding heavy pieces of steel that are being hammered. [Jason]’s vise stands about 3 feet tall, and the main frame components were cut from 1 5/8 inch (41.3 mm) steel with a water jet cutter. The jaws are operated with a large hand wheel connected to a lead screw. Bearings on the lead screw allow the hand wheel to be spun like a flywheel, allowing it to be quickly opened and closed. The weight of the moving jaw keeps the lead screw under tension, eliminating any backlash. This allows for really fine control over the holding force, which [Jason] demonstrates by carefully clamping a tiny screw. With the hand wheel alone the vise can exert 12880 lb / 5800 kg, but a hydraulic lift was also added, boosting the force to 30000 lbs. The deep throat allows a large object to be clamped, and the jaws can also be offset to clamp something to the side of the vise.

The vise was beautifully finished with powder coating and pin striping, which will no doubt wear over time if it’s properly used, but the vise itself should last a few lifetimes. While this isn’t something you can really build in a home workshop, it is always inspiring to see what is possible with a bit more tools, knowledge and skill. The build is documented in a 4 part series (link in first paragraph), but we’ve added a short highlights reel below for your view pleasure.

[Jason] really knows his way around a piece of steel, and we’ve previously covered his techniques for cleaning up the inside to square tubing to make telescoping tubes. Another interesting recent vise build was [Alexandre Chappel]’s wide bench vise that used 3D printed gears to drive two lead screws simultaneously.

source https://hackaday.com/2020/11/05/giant-blacksmith-vise-from-start-to-finish/

A Featherweight Direct Drive Extruder in a Class of Its Own

Even a decade later, homebrew 3D printing still doesn’t stop when it comes to mechanical improvements. These last few months have been especially kind to lightweight direct-drive extruders, and [lorinczroby’s] Orbiter Extruder might just set a paradigm for a new kind of direct drive extruder that’s especially lightweight.

Weighing in at a mere 140 grams, this setup features a 7.5:1 gear reduction that’s capable of pushing filament at speeds up to 200 mm/sec. What’s more, the gear reduction style and Nema 14 motor end up giving it an overall package size that’s smaller than any Nema 17 based extruder. And the resulting prints on the project’s Thingiverse page are clean enough to speak for themselves. Finally, the project is released as open source under a Creative Commons Non-Commercial Share-Alike license for all that (license-respecting!) mischief you’d like to add to it.

This little extruder has only been around since March, but it seems to be getting a good amount of love from a few 3D printer communities. The Voron community has recently reimagined it as the Galileo. Meanwhile, folks with E3D Toolchangers have been also experimenting with an independent Orbiter-based tool head. And the Annex-Engineering crew has just finished a few new extruder designs like the Sherpa and Sherpa-Mini, successors to the Ascender, all of which derive from a Nema 14 motor like the one in the Orbiter. Admittedly, with some similarity between the Annex and Orbiter designs, it’s hard to say who inspired who. Nevertheless, the result may be that we’re getting an early peek into what modern extruders are starting to shape into: smaller steppers and more compact gear reduction for an overall lighter package.

Possibly just as interesting as the design itself is [lorinczroby’s] means of sharing it. The license terms are such you can faithfully replicate the design for yourself, provided that you don’t profit off of it, as well as remix it, provided that you share your remix with the same license. But [lorinczroby] also negotiated an agreement with the AliExpress vendor Blurolls Store where Blurolls sells manufactured versions of the design with some proceeds going back to [lorinczroby].

This is a clever way of sharing a nifty piece of open source hardware. With this sharing model, users don’t need to fuss with fabricating mechanically complex parts themselves; they can just buy them. And buying them acts as a tip to the designer for their hard design work. On top of that, the design is still open, subject to remixing as long as remixers respect the license terms. In a world where mechanical designers in industry might worry about having their IP cloned, this sharing model is a nice alternative way for others to both consume and build off of the original designer’s work while sending a tip back their way.


source https://hackaday.com/2020/11/05/a-featherweight-direct-drive-extruder-in-a-class-of-its-own/

Quadcopter with Tensegrity Shell Takes A Beating And Gets Back Up

Many of us have become familiar with the distinctive sound of multirotor toys, a sound frequently punctuated by sharp sounds of crashes. We’d then have to pick it up and repair any damage before flying fun can resume. This is fine for a toy, but autonomous fliers will need to shake it off and get back to work without human intervention. [Zha et al.] of UC Berkeley’s HiPeRLab have invented a resilient design to do so.

We’ve seen increased durability from flexible frames, but that left the propellers largely exposed. Protective bumpers and cages are not new, either, but this icosahedron (twenty sided) tensegrity structure is far more durable than the norm. Tests verified it can survive impact with a concrete wall at speed of 6.5 meters per second. Tensegrity is a lot of fun to play with, letting us build intuition-defying structures and here tensegrity elements dissipate impact energy, preventing damage to fragile components like propellers and electronics.

But surviving an impact and falling to the ground in one piece is not enough. For independent operation, it needs to be able to get itself back in the air. Fortunately the brains of this quadcopter has been taught the geometry of an icosahedron. Starting from the face it landed on, it can autonomously devise a plan to flip itself upright by applying bursts of power to select propeller motors. Rotating itself face by face, working its way to an upright orientation for takeoff, at which point it is back in business.

We have a long way to go before autonomous drone robots can operate safely and reliably. Right now the easy answer is to fly slowly, but that also drastically cuts into efficiency and effectiveness. Having flying robots that are resilient against flying mistakes at speed, and can also recover from those mistakes, will be very useful in exploration of aerial autonomy.

[IROS 2020 Presentation video (duration 14:16) requires free registration, available until at least Nov. 25th 2020.]

source https://hackaday.com/2020/11/05/quadcopter-with-tensegrity-shell-takes-a-beating-and-gets-back-up/

Rebuilding a Hero (the Robot, not the Sandwich)

When [Scott Baker] found a Heathkit Hero Junior on eBay, he grabbed it. He had one as a kid, but it was long sold. The robot arrived with no electronics, so the first order of business is to give it some new modern brains including an ATMega328 and a Raspberry Pi. You can see the start of the project in the video below.

So far, you can see a nice teardown of the chassis and what’s left of the little robot’s drive system. This wasn’t the big Hero-1 that you probably remember, but it was still a pretty solid platform, especially for the time it was on the market.

[Scott] took over the project from the eBay seller. The original plan included some 3D printed parts to mount a web camera and some other sensors. If you’ve ever wanted to see someone characterize an unfamiliar stepper motor, this is your chance.

We don’t know what happened to the original electronics, but we do know that the original Hero Jr. had a 6808 CPU with a whopping 2 K of RAM and 32 K of ROM. You could upgrade to 24 K of RAM. The original also had an SC-01 speech synthesizer, along with sensors for light and sound. There was also a sonar sensor and two 6 V rechargeable batteries. For the advanced user, you could connect a serial port and use the BASIC cartridge.

By the end of the video, [Scott] could drive the thing around using a joystick. We are sure there’s more to come. Meanwhile, if you want to see the different models Heathkit made over eight years, check out the Old Robots Site. According to them, Heath sold 4,000 of these little monsters along with some 17,000 of the bigger siblings.

We’ve seen Hero upgrades before, of course. Heathkit is back, sort of, although we don’t think we’ll see the likes of the Hero family of robots again anytime soon.

source https://hackaday.com/2020/11/05/rebuilding-a-hero-the-robot-not-the-sandwich/

DualShock Flight Simulator Yoke

Aircraft control interfaces can be divided into stick or yoke, with the stick being more popular for flight simulators. [Akaki Kuumeri] has been designing some ingenious 3D printed adaptors for game console controllers, and his latest build is a yoke adaptor for the PlayStation DualShock Controller.

Like his previous joystick/throttle combination, this yoke makes use of a series of ball and socket links to convert the yoke’s push/pull and rotation motion into the appropriate inputs on the controller’s thumbs sticks. All the components are 3D printed except for rubber bands to provide spring tension. On the sliding contact surfaces between the different components, [Akaki] specifically designed the parts to slide along the grain (layer lines) to allow for smooth motion without resorting to bearings.

If you want an absolute minimalist yoke, tape some potentiometers to a desk drawer. Or you can go to the other end of the scale and build a complete cockpit. With the arrival of Microsoft Flight Simulator 2020, we’ll be seeing a lot of controller builds.

source https://hackaday.com/2020/11/04/dualshock-flight-simulator-yoke/

Building Walks with Robot Legs

The Shanghai Evolution Shift company has just pulled off one of the most impressive robotic projects we’ve ever seen – making a building walk using 198 robotic legs. We’ve all seen structural relocation documentaries where large buildings are moved to new locations. This involves jacking up the building and installing a supporting platform on wheels, then carefully towing the building to its new site.

But the T shape of the five story, 7600 ton Lagena elementary school was problematic, and the route to the new site involved taking a curved path and rotating the building. This ruled out the more traditional methods of relocation. Robot legs came to the rescue. It took 18 days for the building to walk 62 meters and rotate 21 degrees to its new home. This project is part of a trend to preserve historic architecture rather than bulldoze everything to make space for modern buildings.

After watching the video below, we think you’ll agree that this is a unique application of robotics and an amazing engineering feat. Disclaimer – don’t try this at home. Thanks to [Chuckz] for sending us this tip.


Also, you can see a time-lapse video of the move.

source https://hackaday.com/2020/11/04/building-walks-with-robot-legs/

3D Printed Workshop Lamp Uses A Few Neat Tricks

As far as light fittings go, store bought is fine, but it’s hard to beat something you’ve built yourself from the ground up. [Heliox] demonstrates this well, with a 3D-printed workshop lamp that looks the business and is functional, too.

The lamp has plenty of neat design touches that speak to [Heliox]’s experience in the 3D printed arts. The articulating arms are modular, and feature integrated cable guides. The lamp base features nuts inserted mid-print for easy assembly, and the swivel is actually a two-piece mechanism printed as a single assembly. The table clamp uses a large screw, and the benefit of 3D printing means its easy to customise to suit any individual table. Using black and orange filaments gives the lamp a proper industrial look, and the bright LED strips are perfect for illuminating a bench for fine detailed work.

It’s a great addition to [Heliox]’s workspace, and the tall articulated design means it can cast light without getting in the way of what you’re doing. We’ve featured her work before, too – like this glorious infinity cube. Video after the break.

source https://hackaday.com/2020/11/04/3d-printed-workshop-lamp-uses-a-few-neat-tricks/

Minimalist Low Power Supercapacitor Sensor Node

One of the biggest challenges for wireless sensor networks is that of power. Solar panels usually produce less power than you hoped, especially small ones, and designing super low power circuits is tricky. [Strange.rand] has dropped into the low-power rabbit hole, and is designing a low-cost wireless sensor node that runs on solar power and a supercapacitor.

The main components of the sensor node is an ATMega 328P microcontroller running at 4Mhz, RFM69 radio transceiver, I2C temperature/humidity sensor, 1F supercapacitor, and a small solar panel. The radio, MCU, and sensor all run on 1.5-3.6V, but the supercap and solar panel combination can go up to 5.5V. To regulate the power to lower voltage components a low-drop voltage regulator might seem like the simplest solution, but [strange.rand] found that the 3.3V regulator was consuming an additional 20uA or more when the voltage dropped below 3.3V. Instead, he opted to eliminate the LDO, and limit the charging voltage of the capacitor to 3.6V with a comparator-based overvoltage protection circuit. Using this configuration, the circuit was able to run for 42 hours on a single charge, transmitting data once per minute while above 2.7V, and once every three minutes below that.

Another challenge was undervoltage protection. [strange.rand] discovered that the ATmega consumes an undocumented 3-5 mA when it goes into brown-out below 1.8V. The small solar panel only produces 1 mA, so the MCU would prevent the supercapacitor from charging again. He solved this with another comparator circuit to cut power to the other components.

We see challenges like these a lot with environmental sensors and weather stations with smaller solar panels. For communication, low power consumption of a sub-Ghz radio is probably your best bet, but if you want to use WiFi, you can get the power usage down with a few tricks.

source https://hackaday.com/2020/11/04/minimalist-low-power-supercapacitor-sensor-node/

Quick and Simple Milliohmmeter

User [mircemk] presents his “MiliOhm Meter” project which you can build with an Arduino, a handful of common parts from your lab, and a cigar box.  It doesn’t get much simpler than this, folks.  While this is something you won’t be getting calibrated with NIST traceability, it looks like a fun and quick project that’s more than suited for hobbyist measurements.  It’s not only easy to build, the Arduino sketch is less than thirty lines of code.  This is a great learning project, plus you get something useful for your lab when its finished.

We like the creative use of colored tape instead of paint on the project’s box.  If this style suits you, [mircemk] has published several other similar lab instrument projects on his Hackaday.io page, including a frequency meter, an audio spectrum analyzer, and an auto-ranging capacitance meter to name a few.  You might recognize him from some other projects we’ve featured, such as the crazy kinematic arms that set a clock’s hands every minute.


source https://hackaday.com/2020/11/04/quick-and-simple-milliohmmeter/

DIY Heavy Duty Linear Slides

The rise of cost-effective CNC platforms like 3D printers, routers, and laser cutters has gone hand in hand with the availability of affordable and accurate linear rails and extrusions. However, they quickly become expensive when you need something for heavy loads. [Andy Pugh] found himself in need of a large linear slide, so he resorted to making his own with steel square tubing and a bit of PTFE (Teflon).

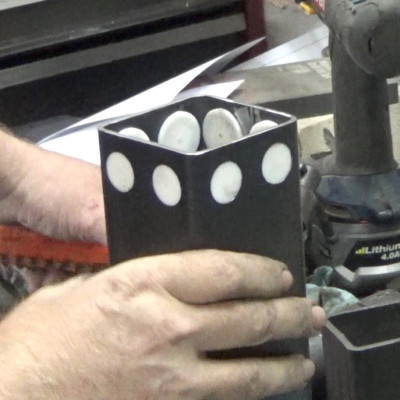
The PTFE slider/spacers

[Andy] needed a compact motorcycle lift for his small workshop, so he designed one with a single vertical tube that mounts on his floor. The moving part of the lift is a slightly larger tube, onto which the motorcycle mounts. To allow the outer part to slide easily [Andy] machined a set of 16 PTFE spacers to fit between the surfaces of the tubes. The spacers have a small shoulder that lets them mount securely in the outer tube without pushing out. After a bit of fine-tuning with a file, it slides smoothly enough for [Andy]’s purposes. With a large lead screw mounted onto the lift, he can easily lift his 200 kg motorcycle with a cordless drill, without taking up all the floor space required by a traditional motorcycle lift.

Although the Teflon spacers will wear with regular use and, they are more than good enough for the occasional motorcycle service, and are also easy to replace. You may not want to use this on your next CNC machine build, but it is a handy blueprint to keep in your mental toolbox for certain use-cases. These spacers were machined on a lathe, but we found that very similar looking PTFE parts are sold as “wrist pin buttons” for the piston of old air cooled VW engines, and could be modified for the purpose.

For other lifting applications, check out this hydraulic workbench, and this forklift for moving stuff in your crawl space without crawling.

source https://hackaday.com/2020/11/04/diy-heavy-duty-linear-slides/