I was reading Joshua Vasquez’s marvelous piece on the capstan equation this week. It’s a short, practical introduction to a single equation that, unless you’re doing something very strange, covers everything you need to know about friction when designing something with a rope or a cable that has to turn a corner or navigate a wiggle. Think of a bike cable or, in Joshua’s case, a moveable dragon-head Chomper. Turns out, there’s math for that!
Basically, the more you wrap a cable or rope around something stationary, the more friction you have to deal with. I put this to good advantage last Spring when my son and I were doing some random tree-climbing with ropes. Turns out that four or five loops of climbing rope against fairly frictiony bark is enough to hold the weight of a grown man, with nothing other than the weight of the rope itself on the other end, for instance. I was also using this effect in a recent wall-plotter-bot design that uses simple cable braid instead of the ubiquitous timing belt.
In none of these cases did I work out the capstan equation with my pocket calculator: four loops around is almost always enough. But by digging into the math and physics, I got more insight. Basically, the friction is an exponential with the angle times the friction coefficient of your cable in the exponent. So what? So, that next turn holds exponentially more weight when you’re climbing. And the grippiness of the tree bark matters in just the same way. You might know this intuitively from experience, but it’s nice to have numbers.
And what’s even better about the insight from doing the math is what doesn’t matter. The radius of the tree falls out, so you can pick a fat branch or a skinny one, as long as it’ll hold your weight!) The fat branch bends less sharply, which gives you less friction per centimeter, but there’s also more centimeters per wrap, and they cancel out. So pick a fatter, rougher tree over a skinnier, smoother one. I would have never thought that!
Here at Hackaday, we’re big fans of rough-and-ready learning by doing. Will this work? Try it out! (If it shouldn’t, and yet it does, it’s a hack.) But there’s also a lot to be said for knowing the underlying math and physics too. Many people think of math as being about crunching numbers, but I find the deeper intuition about which variables in your problem matter, and which don’t at all, infinitely more useful. Learning by doing, guided by a good physical / mathematical intuition, is the best of both worlds. And it saves wear and tear on your mint HP-48G.
This article is part of the Hackaday.com newsletter, delivered every seven days for each of the last 200+ weeks. It also includes our favorite articles from the last seven days that you can see on the web version of the newsletter.
Want this type of article to hit your inbox every Friday morning? You should sign up!
If we had to pick one part to crown as the universal component in the world of analogue electronics, it would have to be the operational amplifier. The humble op-amp can be configured into so many circuit building blocks that it has become an indispensable tool for designers. It’s tempting to treat an op-amp as a triangular black box in a circuit diagram, but understanding its operation gives an insight into analogue electronics that’s worth having. [Mitsuru Yamada]’s homemade op-amp using discrete components is thus a project of interest, implementing as it does a complete simple op-amp with five transistors.
Looking at the circuit diagram it follows the classic op-amp with a long-tailed pair of NPN transistors driving a PNP gain stage and finally a complimentary emitter follower as an output buffer. It incorporates the feedback capacitor that would have been an external component on early op-amp chips, and it has a couple of variable resistors to adjust the bias. Keen eyed readers will notice its flaws such as inevitably mismatched transistors and the lack of a current mirror in the long-tailed pair, but using those to find fault in a circuit built for learning is beside the point. He demonstrated it in use, and even goes as far as to show it running an audio power amplifier driving a small speaker.
Hackers love their ThinkPads. They’re easy to work on, well documented, and offer plenty of potential for upgrades. For the more daring, there’s also a wide array of community-developed modifications available. For example, [Berry Berry Sneaky] has recently put together a step-by-step guide on swapping the common ThinkPad rectangular charging port (also used on ThinkBooks and other Lenovo machines) for USB-C Power Delivery.
Now to be clear, this is not a new concept. But between freely sharing the STL for the 3D printed adapter, providing a full parts list, and providing clear instructions on how to put it all together, [Berry Berry Sneaky] has done a fantastic job of making this particular modification as approachable as possible. For the cost of a common PDC004 Power Delivery “trigger” module and a bit of PETG filament, you can add yet another device to the list of things that work with your shiny new USB-C charger.
While not strictly necessary, [Berry Berry Sneaky] recommends getting yourself a replacement DC input cable for your particular machine before you crack open the case. That will let you assemble everything ahead of time, making the installation a lot quicker. It will also let you keep the original rectangular power jack intact so you can swap it back in if something goes wrong or you decide this whole unified charging thing isn’t quite what you hoped for.
Abstraction is the core of nearly all progress in computing. Unless you are fabricating your own semiconductors and drawing wire, we all create with building blocks ranging from components like CPUs, to operating system functions, to specialized libraries. Just as you wouldn’t want to spend your time deblocking disk records or rendering fonts for output devices, you probably shouldn’t have to think too much about audio data. While there are some powerful audio processing libraries out there, a new embeddable language called SOUL (SOUnd Language) is now in version 1.0 and wants to help you create efficient code for processing audio.
The goal of SOUL is to target a runtime that can run on CPUs, but is better on DSPs. The code aims to be secure and real time with no pointers, garbage collection, and other things that typically interfere with audio processing or security.
The code isn’t hard to puzzle out. Here’s the example for cutting audio volume by half:
[CODE]
processor MinimalGainExample
{
// declare our inputs and outputs:
input stream float audioIn; // mono input stream called “audioIn”
output stream float audioOut; // mono output stream called “audioOut”
// every processor must declare a run() function
void run()
{
const float gain = 0.5f; // a constant to use as our gain factor
loop // (this just loops forever)
{
audioOut << audioIn * gain; // Read the next input sample, multiply by our
// constant, and write it to our output
advance(); // Moves all our streams forward by one frame
}
}
}
[/CODE]
You can see that a processor is essential a thread and can have local and global storage. There are also graphs that assemble different processors with input and output.
Usually, when we want to process audio, we turn to PortAudio just like [Matt] did for his oscilloscope port of Quake. We know of some projects that use Pure Data for audio processing, too.
Most of us make do with the VRAM that came with our graphics cards. We can just wait until the next one comes out and get a little more memory. After all, it’d be madness to try and delicately solder on new components of something so timing-sensitive as RAM chips, right?
[VIK-on] took it upon himself to do just that. The inspiration came when a leaked diagram suggested that the RTX 2000 line could support 16 GB of RAM by using 2GB chips. NVIDIA never did release a 16GB version of the 2070, so this card is truly one of a kind. After some careful scouring of the internet, the GDDR6 chips were procured and carefully soldered on with a hot air gun. A few resistors had to be moved to accommodate the new RAM chips. During power-on, [VIK-on] saw all 16 GB enumerate and was able to run some stress tests. Unfortunately, the card wasn’t stable and started having black screen issues and wonky clocks. Whether it was a bad solder joint or firmware issues, it’s hard to say but he is pretty convinced it is a BIOS error. Switching the resistors back to the 8GB configuration yielded a stable system.
Sometimes, the best hifi gear is the gear you’ve already got. This is particularly the case in the cassette world, as high quality decks are long out of production. [Nick] liked his current rig, but wanted to be able to use it with a remote from across the room. Naturally, he set to hacking the feature in.
The cassette deck in question, a Yamaha K-220, was old enough to lack a remote, but thankfully new enough to use a computer-controlled tape transport. This meant that the basic features of play, stop, rewind and fast forward can all be controlled with simple digital buttons rather than mechanical ones. This made it easy to interface an ATmega328P to the stereo’s original circuitry. Digital IO pins are hooked up to the buttons, held as high-impedance inputs most of the time, only toggling to ground when necessary to trigger a button press. It was then a simple job to hook up an IR receiver to the chip and program it with some Arduino libraries to work with a typical stereo remote control [Nick] had laying around.
Back in the day when most people read the news on wood pulp, newspaper outfits would run off a test print on a small proofing press. This gave them a chance to check for typos before printing off thousands of newspapers on the real press.
These presses can be used for more than letterpress proofing, as [Paul] proves with this DIY version (YouTube, embedded below). They are simple machines that use a heavy roller on bearings to provide uniform pressure, so they’ll work for lino-cut printmaking and aquatint etchings, too.
The roller is the most important bit and is easily the most expensive part of a build like this one. [Paul]’s was fashioned by a UK machinist that he found through ebay. The total cost was £220 (~$300 USD), which is well below the thousand-pound mark where commercial machine prices start.
[Paul] made the base and handle out of plywood and CNC’d the side panels out of aluminium. These side panels contain bearings that hold the roller’s ends in place. As the roller moves back and forth, it slides along on another set of bearings the underside of the press. These bearings ride thin metal rails on the underside of the press so they don’t wear grooves into the wood over time.
[Paul]’s press looks fantastic and looks like it does a great job with everything he throws at it. Some uses require raising up the surface to be printed on to get a good transfer, so [Paul] might make it adjustable in the z-direction at some point in the future. Check out the build and walk-through video after the break.
Sudo is super important Linux utility, as well as the source of endless jokes. What’s not a joke is CVE-2021-3156, a serious vulnerability around incorrect handling of escape characters. This bug was discovered by researchers at Qualys, and has been in the sudo codebase since 2011. If you haven’t updated your Linux machine in a couple days, you may very well be running the vulnerable sudo binary still. There’s a simple one-liner to test for the vulnerability:
sudoedit -s '\' `perl -e 'print "A" x 65536'`
In response to this command, my machine throws this error, meaning it’s vulnerable:
malloc(): corrupted top size

Aborted (core dumped)
To understand the problem with sudo, we have to understand escape characters. It really boils down to spaces in file and folder names, and how to deal with them. You want to name your folder “My Stuff”? That’s fine, but how do you interact with that directory name on the command line, when spaces are the default delimiter between arguments? One option is to wrap it in quotation marks, but that gets old in a hurry. The Unix solution is to use the backslash character as an escape character. Hence you can refer to your fancy folder as My\ Stuff. The shell sees the escape character, and knows to interpret the space as part of the folder name, rather than an argument separator. Escape characters are a common vulnerability location, as there are plenty of edge cases.
Sudo is no exception. The edge case here is a second bug. The sudoedit command launches sudo in editor mode, and is intended to be equivalent to sudo -e. In fact on many systems, sudoedit is a symlink to sudo. The problem is in the command-line parsing code. If you try to invoke sudo with both the -e and -s flags, it treats the command as invalid, and helpfully prints the usage notes. However, when sudoedit is used to launch the editor mode, the -s flag can also be specified, putting sudo into an unintended state, with undefined behavior. After looking over the vulnerability, I’m convinced that this is the more serious of the two bugs. There are likely quite a few other vulnerabilities that could be found as a result of being able to put sudo in two modes of operation at once.
The other problem is how sudo handles an escape character with no following character to escape. The code hops over the null string termination, and keeps copying characters. In a normal usage mode, this code is impossible to execute in this strange way, but because of the odd dual-mode state, this bug can be exploited.
Updated versions of sudo have shipped in the major distros, so make sure you update! Thankfully, while there is a proof-of-concept one-liner that will crash sudo, no actual exploit code has been published. There will likely be full exploit POCs available soon, though.
Load a Webpage, Get iPwned
Apple has published an advisory about what appears to be an attack chain found in the wild against the iOS platform. The chain is a trio of CVEs, two in webkit and one in the kernel. This is likely the work of yet another state-sponsored actor, who put the attack chain together to gather information on a specific group of people. The two webkit CVEs are probably an initial RCE and a sandbox escape. The kernel vuln is then used to elevate to system privileges and run the spyware. It’s typical to see these malware packages run in memory only, and not make any permanent modifications to the device’s OS. If the rest of the story gets released, we can come back and check my guesses for accuracy.
Brazill Leaks Entire Taxpayer Database
It may not be the biggest database leak for raw size, but this must set a per capita record. One of Brazil’s government agencies seems to have let their database escape (in Portuguese), as a whopping 220 million records of CPF number, full name, and date of birth are floating around the shadier side of the internet. This is probably the identifying information of every Brazilian citizen alive, and even some who are no longer with us, because their official population is only 213 million. While the immediate uses for targeted phishing and fraud is obvious, it will be interesting to see what the long term effects are of publishing the equivalent of everyone’s social security number.
Recently both a Synology user, and a QNAP user discovered a dovecat process pegging their device processors at 100%. What is this strange process, clumsily trying to look like an innocent mail daemon?
Thankfully [Matthew Ruffel] has already done an analysis on this malware. Dovecat is nothing more than the open source XMRig crypto miner, with some hard coded configuration. It’s very possible that any system that has a dovecat process also has the “hy4” malware on it. What might be the most fascinating about this little crypto-mining malware campaign is that it seems to be targeting NAS devices. Alternatively, it may be simply targeting SSH servers with weak passwords.
NetWalker Takedown
The image to the right caught my attention, as there have just been a handful of successful TOR page takedowns like this. The NetWalker infrastructure has been seized, along with over $450,000 in cryptocurrency. A Canadian citizen has been arrested as part of the operation.
Krebs has more details on this story. NetWalker is a ransomware system, and has been called “ransomware-as-a-service”. It remains to be seen if the head of this particular snake has been cut off, or if instead it’s a hydra, and will pop right back up.
Odds’n’ends
VLC has released version 3.0.12. Most of the changelog is normal bug fixes, with support for Apple designed processors being the stand-out new feature, do note that this release also fixed “some security issues”. What issues might those be? While we don’t have the details spelled out, the security bulletin points out a pair of buffer overflows and some invalid pointers being dereferenced. Put clearly, these bugs could probably be used to build an exploit that triggers as a result of viewing a video.
The IObit forums were breached recently, and the user database is being used to spread ransomware. To make the whole scheme seem even more legitimate, the attacker hosted the malicious installer on the compromised site. Here’s where the story takes a humorous turn. The ransom process is also a crypto-currency ponzi scheme! You send us 200 DERO coins to decrypt your files, and once DERO hits $100 a coin, we’ll send you back $500 worth of the coin. It’s a 5X return on your investment!
Drupal just released an update that fixes a potentially severe vulnerability. The Archive_Tar library is used in Drupal core, and contained a directory traversal vulnerability, CVE-2020-36193. This usually means that even if an archive is unzipped in a safe directory, it can overwrite important files elsewhere on the server. Regardless, Drupal considers this a critical issue, and recommends updating right away.
For as long as super-heroes have existed, they have inspired hacker projects. For [Everett Bradford], emulating the character Pyro from X-Men has been an on and off project for the last decade. His latest version, Pyro System V4, integrates quite a bit of control electronics to give the rather convincing effect of mind-controlled fire in the palm of his hand. (Video, embedded below.)
The system is a motor-actuated slider strapped to [Everett]’s forearm, which pushes a pivoting end-effector with an integrated butane burner into the palm of his hand. The slider runs on 4 mm linear bearings actuated by a small geared DC motor using cables. The end effector is spring-loaded to push it into the palm and integrates a high voltage ignition arc generator circuit, nozzle, and capacitive activation button.
The butane gas canister and the valve was cannibalized from a small blow torch lighter, and the valve is actuated by another geared DC motor. The valve actuator, slide actuator, and end-effector hinge all integrate position feedback via hall effect sensors and magnets. The sensor in the hinge allows the slide to actively correct for the angle of the user’s wrist, keeping the end effector in the middle of the palm.
The control circuit is split into two parts. One PIC16 microcontroller runs all the motion control and position sensing, while a PIC18 connected to a small touch screen handles user interface, control parameters, and ignition. The touch screen proved especially useful for control parameters during development without needing to connect to a laptop.
Some of [Everett]’s previous version had a much more impressive (and dangerous) flame but was also very bulky. We think this latest version strikes a pretty good balance regarding compactness and achieving convincing illusion.
The Raspberry Pi Pico is the latest product in the Raspberry Pi range, and it marks a departure from their previous small Linux-capable boards. The little microcontroller board will surely do well in the Pi Foundation’s core markets, but its RP2040 chip must have something special as a commercial component to avoid being simply another take on an ARM microcontroller that happens to be a bit more expensive and from an unproven manufacturer in the world of chips. Perhaps that special something comes in its on-board Programable IO perhipherals, or PIOs. [CNX Software] have taken an in-depth look at them, which makes for interesting reading.
The PIOs are a set of state machines that have their own simple assembly language to execute simple repetitive I/O tasks without requiring the attention of the main processor core. How they can be configured is up to the imagination of the programmer, but examples suggested are extra I2C or SPI buses, or video interfaces. We expect the hacker community to push them to extremes with unexpected applications, much as has happened with the ESP32’s I2S peripheral. The article introduces the assembly language, then gives us simple examples in assembler, C/C++, and Python. If you have a Raspberry Pi Pico then you’ll surely be wanting to have a play with the PIOs, and we look forward to seeing what you come up with.
Quadcopters have incredible flying abilities, but if one loses just a single motor, it drops like a rock. Researchers from the University of Zurich’s Robotics and Perception Group have proven that this does not need to be the case by keeping a quadcopter flying with only three motors.
A quadcopter usually has enough thrust to stay aloft with only three motors, but it will spin uncontrollably in the yaw axis. It is impossible to stop a quadcopter from spinning, so the focus for researchers was on keeping the drone controllable while it’s spinning. To achieve this, accurate position and motion estimation is required, so they attached a pair of cameras to the bottom of the craft for visual-inertial odometry (VIO). One is a normal optical camera, while the other is an event camera, which has pixels that can independently respond to changes in light as they occur. This means that it has better low light performance and does not suffer from motion blur.
The feeds from the cameras are analyzed in real-time by an onboard Nvidia Jetson TX2 for state estimation, which is then used with an optical range sensor and onboard IMU to maintain controlled flight, as demonstrated in the video after the break. The research paper is free to read, and all the code is available on GitHub.
Randonauting is the pastime of using random numbers to generate a destination to visit, in the pursuit of adventure. Of course, anything that can be done on a website with a script is even cooler with custom hardware, so [Decker] built a rig for the job.
The device uses a USB hardware random number generator to produce truly random numbers through quantum effects; at least, according to our best theories of the universe. These numbers are then used to pick a random set of GPS coordinates and a time in which to be there, a fun twist on traditional Randonauting of [Decker]’s own creation.
At its heart, it’s a random number generator pumped through some Python scripts. Where this build elevates itself is not in the mechanics, but the presentation. The rig runs on a Raspberry Pi, inside a bell jar, with a vacuum fluorsecent display, fairy lights and plumbing components. It plays on the cyberpunk aesthetic, and it’s so much harder to ignore one’s mission when the time and place are given in glowing numerals by an enigmatic, mysterious machine.
The leading cause of xenotransplant rejection is a sugar called alpha-gal. This sugar appears on the cell surfaces of all non-primate mammals. Alpha-gal is problematic for other reasons, too: a condition called alpha-gal syndrome usually begins when a Lone Star tick bites a person and transmits alpha-gal cells from the blood of animals they have bitten. From that point on, the person will experience an allergic reaction when eating red meat such as beef, pork, and lamb.
Pigs with Purpose
A litter of lifesaving piglets. Image via Revivicor
More people need a kidney than any other organ, so the company plans to start human trials with kidneys and move on to heart transplants in the future. In December 2020, the Food and Drug Administration (FDA) certified these so-called GalSafe pigs as fit for human consumption and therapeutic use. Although Revivicor doesn’t intend to produce GalSafe pigs for an allergy-free alternative for people with alpha-gal syndrome anytime soon, the door is certainly open for other companies to do so.
In 2016, Revivicor and researchers from the National Institutes of Health reported that they had been able to keep pigs’ hearts alive inside baboons for two and a half years. However, these weren’t direct transplant situations — the baboons kept their original hearts and hosted the pigs hearts in their abdomens.
Genetically modified alpha-gal-free pigs could help the organ transplant crisis, though it’s unclear at this point how long the organs will last once transplanted into humans. Revivicor and United Therapeutics hope they can last the rest of a person’s life, or at least long enough until they can get a human organ to replace it. Even if this only ends up being a stopgap until a better alternative arives, it could save many lives. What do you think?
The basic test instrument suite — a bench power supply, a good multimeter and perhaps an oscilloscope — is extremely flexible, but not exactly “plug and play” when it comes to diagnosing problems with some common hardware setups. A problem with a servo driver, for example, might be easy enough to sort of with a scope, but setting everything up to see what’s going on with the PWM signal takes some time.
There’s got to be a better way to diagnose hobby electronics woes, and if [Bob Alexander] has his way, his “Logic Meter”, or something very close to it, will be the next must-have bench tool. The Logic Meter combines some of the functionality of an oscilloscope and a logic analyzer into a handy instrument that’s as easy to use as a multimeter. The Logic Meter’s probes connect to logic-level signals in a circuit and can be set up to capture or send serial data, either directly to or from a UART or via an SPI bus connection. There are also functions for testing servos and similar devices with a configurable PWM output. [Bob] rounds out the functionality with a GPS simulator and a simple logic analyzer, plus some utility functions.
The beauty part of the Logic Meter is that [Bob] has left where it goes next largely up to the community. He’s got a GitHub repo with details on the PIC32-based hardware, and the video below makes it clear that this is just a jumping-off point to further work that he hopes results in a commercial version of the Logic Meter. That’s a refreshing attitude, and we hope it pays off; from the look of a few of [Bob]’s retrocomputing makeovers, something like the Logic Meter could come in pretty handy.
When it was first announced, many people were skeptical of the Nintendo DS. Rather than pushing raw power, the unique dual screen handheld was designed to explore new styles of play. Compared to the more traditional handhelds like the Game Boy Advance (GBA) or even Sony’s PlayStation Portable (PSP), the DS seemed like huge gamble for the Japanese gaming giant.
But it paid off. The Nintendo DS ended up being one of the most successful gaming platforms of all time, and as [Modern Vintage Gamer] explains in a recent video, at least part of that was due to its surprising graphical prowess. While it was technically inferior to the PSP in almost every way, Nintendo’s decades of experience in pushing the limits of 2D graphics allowed them to squeeze more out of the hardware than many would have thought possible.
On one level, the Nintendo DS could be seen as a upgraded GBA. Developers who were already used to the 2D capabilities of that system would feel right at home when they made the switch to the DS. As with previous 2D consoles, the DS had several screen modes complete with hardware-accelerated support for moving, scaling, rotating, and reflecting up to four background layers. This made it easy and computationally efficient to pull off pseudo-3D effects such as having multiple backdrop images scrolling by at different speeds to convey a sense of depth.
On top of its GBA-inherited tile and sprite 2D engine, the DS also featured a rudimentary GPU responsible for handling 3D geometry and rendering. Hardware accelerated 3D could only used on one screen at a time, which meant most games would keep the closeup view of the action on one display, and used the second panel to show 2D imagery such as an overhead map. But developers did have the option of flipping between the displays on each frame to render 3D on both panels at a reduced frame rate. The hardware can also handle shadows and included integrated support for cell shading, which was a particularly popular graphical effect at the time.
By combining the 2D and 3D hardware capabilities of the Nintendo DS onto a single screen, developers could produce complex graphical effects. [Modern Vintage Gamer] uses the example of New Super Mario Bros, which places a detailed 3D model of Mario over several layers of moving 2D bitmaps. Ultimately the 3D capabilities of the DS were hindered by the limited resolution of its 256 x 192 LCD panels; but considering most people were still using flip phones when the DS came out, it was impressive for the time.
Compared to the Game Boy Advance, or even the original “brick” Game Boy, it doesn’t seem like hackers have had much luck coming up with ways to exploiting the capabilities of the Nintendo DS. But perhaps with more detailed retrospectives like this, the community will be inspired to take another look at this unique entry in gaming history.
Space is hard, especially if you haven’t done it before. A growing number of CubeSats are launched by small, inexperienced teams every year, and a number of them fail due to missing some small but critical hardware or software problem. Researchers from the Robotic Exploration Lab (REx) at Carnegie Melon University have learned some of these lessons the hard way and created PyCubed, an open-source hardware and software framework for future CubeSats.
Most satellites, including CubeSats, require the same basic building blocks. These include ADCS (Attitude Determination and Control System), TT&C (telemetry, track, and command), C&DH (command and data handling), and an EPS (electrical power system). Each of these building blocks is integrated into a single PC/104 size PCB. The main microcontroller is an ATSAMD51, also used on a couple of Adafruit dev boards, and runs Circuit Python. Communications are handled by a LoRa radio module, and there is also an unpopulated footprint for a second radio. An LSM9DS1 IMU and an optional GPS handle navigation and attitude determination, and a flash chip and micro SD card provide RAM and data storage. The EPS consists of an energy harvester and battery charger, power monitor, and regular, that can connect to external Li-Ion batteries and solar panels. Two power relays and a series of MOSFETs connected to burn wires are used to deploy the CubeSat and its antennas.
On the PCB there are standardized footprints for up to four unique payloads for the specific missions. The hardware and software are documented on GitHub, including testing and a complete document on all the design decisions and their justifications. The PyCubed was also presented at the 2019 AIAA/USU Conference on Small Satellites. The platform has already been flight-tested as part of the Kicksat-2 mission, and will also be used in the upcoming V-R3X, Pandasat, and Pycubed-1 projects.
This is not the first open-source CubeSat we’ve seen, and we expect these platforms to become more common. Tracking a CubeSat is a lot less expensive than sending one to space, and can be done for as little as $25.
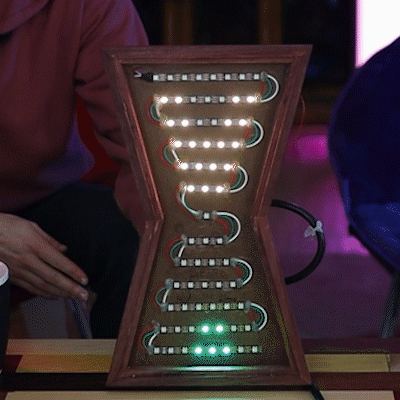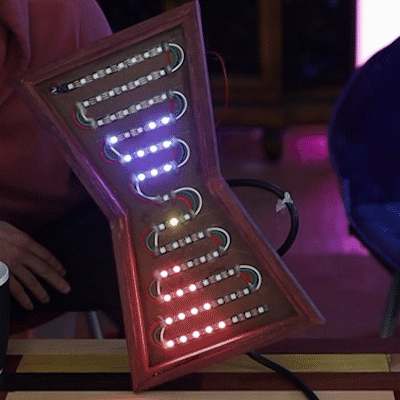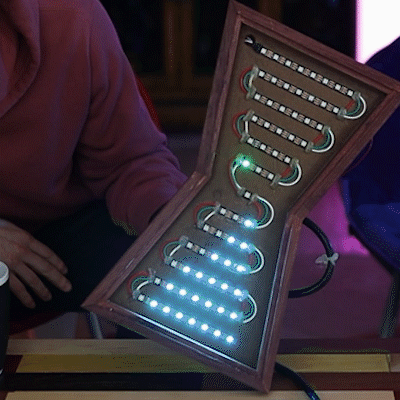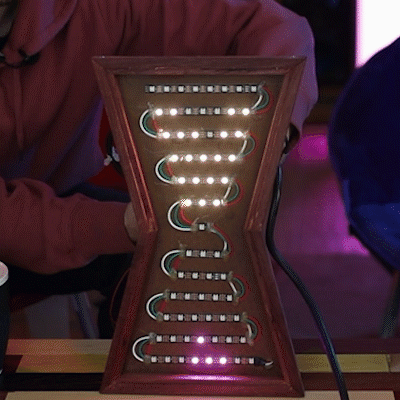
If you want to waste time in a meaningful way, get yourself an hourglass. It’s simultaneously mesmerizing and terrifying to sit there and watch the seconds slip through the threshold that separates possibility from missed opportunity.
[Ty and Gig]’s LED hourglass is equally beautiful to watch. It doesn’t actually tell time, but that’s perfectly fine by us. What it does do is animate the LEDs to approximate grains of sand in gravity, no matter how the hourglass is tilted.
In either vertical orientation, the sand falls as long as there is some in the top. When the hourglass is horizontal, the LEDs settle just like real sand does. [Ty and Gig] achieved this with a whole lot of code that breaks the animation frames into structure arrays.
By contrast, the hardware part of this build is fairly simple: all that’s needed to replicate this build is some RGB LEDs a beefy power supply to drive them, an accelerometer, and a microcontroller.
[Ty and Gig] were planning to use an ESP8266, but misplaced it and went with an Arduino Mega instead. (You know what they say — buy a replacement and the one you lost will turn up almost immediately.) The beautiful frame is made from leftover purpleheart, a hardwood that turns purple with exposure to air. Check out the build video after the break.
The Apple Watch was the tech company’s attempt to bring wrist computers into the mainstream. It’s naturally available in a variety of fits and finishes, but if you want something properly original, you’ve got to go custom. [Useless Mod] does just that with a clear case for the popular smartwatch.
The mod starts with a patient, careful disassembly of the watch – necessary given the delicate components inside. It’s achieved in the end with only having to drill out 1 screw and an unfortunately snapping of the crown wheel axle. However, [Useless Mod] presses on, and silicone casts the original Apple enclosure. The video goes over all the finer points, from degassing to using strips of acrylic plastic to act as runners. Once done, the silicone mold is used to produce a replica case in transparent epoxy, and the watch is reassembled.
The final result is impressive, with the case optically clear and showing off the watch’s internals. The look is improved by removing some of the original insulation tape to better reveal the PCBs inside. Unfortunately, the design of the watch, which is largely covered by a screen and heartbeat sensor, means it’s not the greatest choice for a clear case mod, but it works nonetheless. We’ve seen similar work before from [Useless Mod] too – like this transparent drone case for the Mavic Mini. Video after the break.
You’d be forgiven for thinking that receiving data transmissions from orbiting satellites requires a complex array of hardware and software, because for a long time it did. These days we have the benefit of cheap software defined radios (SDRs) that let our computers easily tune into arbitrary frequencies. But what about the software side of things? As [Dmitrii Eliuseev] shows, decoding the data satellites are beaming down to Earth is probably a lot easier than you might think.
Well, at least in this case. The data [Dmitrii] is after happens to be broadcast from a relatively old fleet of satellites operated by the National Oceanic and Atmospheric Administration (NOAA). These birds (NOAA-15, NOAA-18 and NOAA-19) are somewhat unique in that they fly fairly low and utilize a simple analog signal transmitted at 137 MHz. This makes them especially good targets for hobbyists who are just dipping their toes into the world of satellite reception.
[Dmitrii] doesn’t spend a lot of time talking about the hardware in this post, only to say that he’s using a SDRPlay with what he describes as a poor antenna. He provides a link for information on building a more suitable antenna, but the signal is strong enough that an old set of “Rabbit Ears” will do in a pinch. From there he goes over how you can predict when one of the NOAA birds will be passing overhead, and explains how to configure your SDR software to capture the resulting signal. From there, it’s a step-by-step guide on how to make sense of the recorded WAV file.
With the help of the scipy library, it’s surprisingly easy to load the WAV file and generate some visualizations of the signal within. Since it’s analog, it only takes a bit more work with the Python Imaging Library (PIL) to convert that into a 2D image. [Dmitrii] notes that using the putpixel function isn’t the most efficient way to do this, and gives some tips on how you could speed up the process greatly, but for the purposes of the demonstration it makes for more easily understood code.
As much as we love Star Trek, we have to admit there are some continuity problems. For example, in Spock’s Brain, the alien-of-the-week’s ion drive gave Scotty engineering envy. However, in The Menagerie, the computer identifies a Starfleet shuttlecraft as having ion propulsion. Either way, ion propulsion is real and NASA has toyed with it for ages and many satellites use it for maintaining orbit. Now researchers from MIT and the Monterrey Institute of Technology and Higher Studies 3D printed tiny ion engines.
The engine is about the size of a dime and, like all ion engines, produces tiny amounts of thrust. In fact, the researchers liken it to half the weight of one sesame seed from a hamburger bun. However, in space, these tiny thrusts add up and over time can produce significant acceleration.
The full paper is available and shows the device operates electrohydrodynamically, creating a fine spray of charged particles. Interestingly, the device is capable of creating fine sprays of liquid or nanofibers, so the applications aren’t just for space vehicles. However, the researchers were actually surprised that the device creates a pure ion jet and they aren’t entirely sure how the device works.
The device has a reservoir of liquid with an array of emitter cones. The cones are coated with zinc oxide nanowires that act as wicks to transfer the liquid to the emitter tips where the liquid is ionized and expelled. The researchers think the nanowires are responsible for the creation of the pure jet of ions.

 Basically, the more you wrap a cable or rope around something stationary, the more friction you have to deal with. I put this to good advantage last Spring when my son and I were doing some random tree-climbing with ropes. Turns out that four or five loops of climbing rope against fairly frictiony bark is enough to hold the weight of a grown man, with nothing other than the weight of the rope itself on the other end, for instance. I was also using this effect in a recent wall-plotter-bot design that uses simple cable braid instead of the ubiquitous timing belt.
 . But by digging into the math and physics, I got more insight. Basically, the friction is an exponential with the angle times the friction coefficient of your cable in the exponent. So what? So, that next turn holds exponentially more weight when you’re climbing. And the grippiness of the tree bark matters in just the same way. You might know this intuitively from experience, but it’s nice to have numbers.


 The image to the right caught my attention, as there have just been a handful of successful TOR page takedowns like this.