Booting a PC from Vinyl for a Warmer, Richer OS

If you’ve scrolled through the list of boot options offered on any PC’s BIOS, it reads like a history of storage technology. Up top we have the options to boot from disk, often a solid-state drive, then USB disk, optical drive, removable media, and down the bottom there’s usually an option to boot from the network. Practically no BIOS, however, has an option to boot a PC from a vinyl record — at least until now.

Clearly a project from the “Because why not?” school of hacking, [Jozef Bogin] came up with the twist to the normal booting process for an IBM-PC. As in the IBM-PC — a model 5150, with the putty-colored case, dual 5-1/4″ floppies, and one of those amazing monochrome displays with the green slow-decay phosphors. To pull off the trick, [Jozef] leverages the rarely used and little known cassette tape interface that PCs had back in the early days. This required building a new bootloader and burning it to ROM to make the PC listen to audio signals with its 8255 programmable peripheral interface chip.

Once the PC had the right bootloader, a 64k FreeDOS bootable disk image was recorded on vinyl. [Jozef] provides infuriatingly little detail about the process other than to mention that the audio was sent directly to the vinyl lathe; we’d have loved to learn more about that. Nonetheless, the resulting 10″ record, played back at 45 RPM with some equalization tweaks to adapt for the RIAA equalization curve of the preamp, boots the PC into FreeDOS just fine, probably in no more time than it would have taken to boot from floppy.

It’s may not be the first time we’ve seen software on vinyl, but it’s still a pretty cool hack. Want to try it yourself but lack a record-cutting lathe? Maybe laser-cutting your boot disc will work.

Thanks to [John] and a bunch of other folks who tipped us off on this one.

source https://hackaday.com/2020/11/23/booting-a-pc-from-vinyl-for-a-warmer-richer-os/

The Most Annoying Among Us Tasks Created In Real Life

Among Us is a hit game of deception and intrigue. Those who have played it know the frustration of trying to complete some of the intentionally difficult tasks onboard the Skeld. [Zach Freedman] decided to recreate some of these in real life.

[Zach] built what are arguably the three most frustrating tasks from the game. There’s the excruciatingly slow upload/download station built out of an old Samsung tablet and an NFC tag, and the reactor start console created using a Raspberry Pi 3B, Teensy 3.2, and a custom mechanical keyboard. But perhaps most annoying of all is the infamous card reader. Built with another Teensy, it requires the user to swipe their ID card at just the right speed, except that speed is randomly generated for every swipe. Also, the machine fails 20% of good swipes just because. Perhaps what we love most is the way [Zach] recreated the classic VFD look by putting an OLED display behind bottle-green plastic and using a 14-segment font.

It’s a fun homage to a wildly successful indie game, and we could imagine these props would be a hit at a makerspace party. We’ve featured other Among Us themed builds before, too. Video after the break.

source https://hackaday.com/2020/11/22/the-most-annoying-among-us-tasks-created-in-real-life/

Hackaday Links: November 22, 2020

Remember DSRC? If the initialism doesn’t ring a bell, don’t worry — Dedicated Short-Range Communications, a radio service intended to let cars in traffic talk to each other, never really caught on. Back in 1999, when the Federal Communications Commission set aside 75 MHz of spectrum in the 5.9-GHz band, it probably seemed like a good idea — after all, the flying cars of the future would surely need a way to communicate with each other. Only about 15,000 vehicles in the US have DSRC, and so the FCC decided to snatch back the whole 75-MHz slice and reallocate it. The lower 45 MHz will be tacked onto the existing unlicensed 5.8-MHz band where WiFi now lives, providing interesting opportunities in wireless networking. Fans of chatty cars need not fret, though — the upper 30 MHz block is being reallocated to a different Intelligent Transportation System Service called C-V2X, for Cellular Vehicle to Everything, which by its name alone is far cooler and therefore more likely to succeed.

NASA keeps dropping cool teasers of the Mars 2020 mission as the package containing the Perseverance rover hurtles across space on its way to a February rendezvous with the Red Planet. The latest: you can listen to the faint sounds the rover is making as it gets ready for its date with destiny. While we’ve heard sounds from Mars before — the InSight lander used its seismometer to record the Martian wind — Perseverance is the first Mars rover equipped with actual microphones. It’s pretty neat to hear the faint whirring of the rover’s thermal management system pump doing its thing in interplanetary space, and even cooler to think that we’ll soon hear what it sounds like to land on Mars.

Speaking of space, back at the beginning of 2020 — you know, a couple of million years ago — we kicked off the Hack Chat series by talking with Alberto Caballero about his “Habitable Exoplanets” project, a crowd-sourced search for “Earth 2.0”. We found it fascinating that amateur astronomers using off-the-shelf gear could detect the subtle signs of planets orbiting stars half a galaxy away. We’ve kept in touch with Alberto since then, and he recently tipped us off to his new SETI Project. Following the citizen-science model of the Habitable Exoplanets project, Alberto is looking to recruit amateur radio astronomers willing to turn their antennas in the direction of stars similar to the Sun, where it just might be possible for intelligent life to have formed. Check out the PDF summary of the project which includes the modest technical requirements for getting in on the SETI action.

A few months ago we reported that Boston Dynamics was finally finding customers with use cases that fit their flagship product, the “Big Dog” robot nicknamed Spot. The customer was Ford and the application involved periodic surveys of their enormous transmission plant, normally performed by engineers. At the same time, BP was training Spot for a far more dangerous job: oil rig inspections. Normally, operators on offshore oil platforms make the rounds several times a day to spot anything out of the ordinary: leaks, corrosion, or other situations that can pose a hazard to the platform and the people on it. After oil rig simulator training, Spot moved on to BP’s “Mad Dog” rig in the Gulf of Mexico, where it wanders about making sure everything’s copacetic. They’ve even trained Spot to read gauges and discern valve handle positions, and they’ve equipped the robot with sensors for methane to detect leaks.

And finally, how about a little high-voltage fun? Jay Bowles over at Plasma Channel just released a new video where he explores electrostatic levitation. We had Jay on for a Hack Chat not too long ago where we discussed his passion for plasma. The new video doesn’t have much plasma, but it does focus on how to use a 70-kV voltage multiplier to float scraps of tinfoil in the air. Jay even throws himself into the circuit at one point, levitating things with his bare hands. It seems like good fun, even if we wouldn’t recommend it as particularly safe.

source https://hackaday.com/2020/11/22/hackaday-links-november-22-2020/

Espressif Leaks ESP32-C3: A WiFi SoC That’s RISC-V and is ESP8266 Pin-Compatible

Six years on from the emergence of the Espressif ESP8266 we might believe that the focus had shifted to the newer dual-core ESP32. But here comes a twist in the form of the newly-revealed ESP32-C3. It’s a WiFi SoC that despite its ESP32 name contains a RISC-V core in place of the Tensilica core in the ESP32s we know, and uses the ESP8266 pin-out rather than that of its newer sibling. There’s relatively little information about it at the time of writing, but CNX Software have gathered together what there is including a draft datasheet whose English translation is available as a Mega download. As with other ESP32 family members, this one delivers b/g/n WiFi and Bluetooth Low-Energy (BLE) 5, where it differs is the RISC-V 32 Single-core processor with a clock speed of up to 160 MHz. There is 400 kB of SRAM and 384 kB ROM storage space built in.

While there is no official announcement yet, Espressif has been dropping hints. There’s been an OpenOCD configuration file for it in the Espressif repositories since the end of last month. And on Friday, Espressif Software Engineering Manager [Sprite_TM] answered a reddit comment, confirming the RISC-V core.

ESP-01: Kjerish, CC BY-SA 4.0, RISC-V logo: RISC-V foundation, Public domain.

Why they are releasing the part as an ESP32 rather than giving it a series number of its own remains a mystery, but it’s not hard to see why it makes commercial sense to create it in an ESP8266-compatible footprint. The arrival of competing parts in the cheap wireless SoC space such as the Bouffalo Labs BL602 we mentioned recently is likely to be eating into sales of the six-year-old chip, so an upgrade path to a more capable part with minimal new hardware design requirements could be a powerful incentive for large customers to stay with Espressif.

We’re left to guess on how exactly the rollout will proceed. We expect to see similar developer support to that they now provide for their other chips, and then ESP32-C3 powered versions of existing ESP8266 boards in short order. It’s also to be hoped that a standard RISC-V toolchain could be used instead of the device-specific ones for current Espressif offerings. What we should not expect are open-source replacements for the blobs that drive the on-board peripherals, as the new chip will share the same closed-source IP as its predecessors for them. Perhaps if the PINE64 initiative to reverse engineer blobs for the BL602 bears fruit, we might see a similar effort for this chip.

source https://hackaday.com/2020/11/22/espressif-leaks-esp32-c3-a-wifi-soc-thats-risc-v-and-is-esp8266-pin-compatible/

DOOM Running on the Nintendo Game & Watch

Today the newly-released Nintendo Game & Watch can play DOOM. Sure, there are caveats…this is a watered down version due to the restraints of the hardware itself. But the important thing is that this shows the hardware has been fully owned. This is code written to replace the firmware that ships on the STM32 within, and that makes this a gorgeous little hardware platform that is completely open to homebrew hacking.

Honestly, you had to assume this was going to happen pretty quickly considering the effort being thrown into it. We first reported on Tuesday that the EEPROM memory which stores the ROMs on the Game and Watch had been decoded. Shortly after that was published, [stacksmashing] and [Konrad Beckmann] were showing test patterns on the display and mentioning the audio was working as well. Turns out they were able to dump the stock firmware despite the chip being security locked.

We’ll have to wait for more details on exactly how to dump firmware, but [stacksmashing] drops enough of a mention in the video below to confirm the obvious. A common approach to dumping code from a locked microcontroller is to find a vulnerability that grants execution of custom code. Being able to run just a few lines of your own code is enough set up something as simple as looping through all internal flash memory addresses and dumping them over a few GPIO pins. In this case our two heroes discovered some ARM code was being loaded from the EEPROM onto the STM32, and managed to inject their own directives to perform the dump. They have promised full details soon.

What we have today is a pretty tricky hack not just to load code, but to get DOOM to run on meager hardware specs. Notably, 128 k of SRAM and 1.3 MB of external RAM. There’s also a bottleneck with the 1.1 MB of FLASH for storing game files. The textures were stripped down, and memory allocation was rewritten, but the proof of concept is there and the game runs. Homebrew, here we come!

[Thanks @arturo182]

source https://hackaday.com/2020/11/22/doom-running-on-the-nintendo-game-watch/

Artistic Robot Has Paints, Will Travel

Creativity is a very human trait, and one that many try to emulate with robots. Some focus on the cerebral side of things, working with neural networks and machine learning to produce new artistic output. Others work on the mechanical side, building ‘bots that can manipulate tools in the real world for artistic purposes. [Technovation]’s latest build falls into the latter category – a small Arduino-powered ‘bot that likes to paint.

The robot moves around on two wheels, each driven by a stepper motor for accurate movement. The paintbrush itself is controlled with another stepper, which rotates it between the paint pots and the canvas. A servo is used to dip the brush into pots, and to apply it to the canvas. An Arduino Uno runs the show, with the robot currently programmed to paint random lines of various colors on the canvas.

By virtue of its roving design, it could theoretically paint on arbitrarily large canvasses. It’s a platform that could prove highly capable when paired with a neural network and perhaps some machine vision to allow it to concoct more complex artworks. We’ve seen other paint bots before, too. Video after the break.

source https://hackaday.com/2020/11/22/artistic-robot-has-paints-will-travel/

Blue Pill as a Nerdy Swiss Army Knife

Not everyone can afford an oscilloscope, and some of us can’t find a USB logic analyzer half the time. But we can usually get our hands on a microcontroller kit, which can be turned into a makeshift instrument if given the appropriate code. A perfect example is buck50 developed by [Mark Rubin], an open source firmware to turn a STM32 “Blue Pill” into a multi-purpose test and measurement instrument.

buck50 comes with a plethora of functionality built in which includes an oscilloscope, logic analyzer, and bus monitor. The device is a two way street and also comes with GPIO control as well as PWM output. There’s really a remarkable amount of functionality crammed into the project. [Mark] provides a Python application that exposes a text based UI for configuring and using the device though commands and lots of commands which makes this really nerdy. There are a number of options to visualize the data captured which includes gnuplot, gtk wave and PulseView to name a few.

[Mark] does a fantastic job not only with the firmware but also with the documentation, and we really think this makes the project stand out. Commands are well documented and everything is available on [GitHub] for your hacking pleasure. And if you are about to order a Blue Pill online, you might want to check out the nitty-gritty of the clones that are floating around.

Thanks [JohnU] for the tip!

source https://hackaday.com/2020/11/22/blue-pill-as-a-nerdy-swiss-army-knife/

RGB Party Bike Flashes With The Beat

One of the biggest dangers to a cyclist is not being seen at night. To counteract this, all manner of lighting and reflective gear is available to help ensure bicycles are seen on the streets. Of course, you don’t have to stop at the purely practical. [TechnoChic] decided to have some fun with her ride, festooning her party bike with many, many LEDs.

As you’d expect, the RGB illuminations are thanks to WS2812B LED strips. Running the show is  a trio of Arduino Nano 33 IoTs – one for the LEDs on the bike’s frame, the other two mounted on the front and back wheels respectively. This allowed for the easy control of LEDs on the spokes without having to pass data and power lines to the rotating wheels. The LEDs on the frame are even music-reactive, with the Arduino sampling music input via one of its analog-to-digital converters.

Paired with a boombox on the bike, the build makes for a great way to hype up group rides through the city at night. We can imagine such a bike being an absolute hit at Critical Mass, though you’ve probably gotta add a laser or glitter cannon if you’re going to draw attention at Burning Man. If you’re tired of pedaling, you might consider an electric conversion, too. Video after the break.

source https://hackaday.com/2020/11/22/rgb-party-bike-flashes-with-the-beat/

Intel’s Forgotten 1970s Dual Core Processor

Can you remember when you received your first computer or device containing a CPU with more than one main processing core on the die? We’re guessing for many of you it was probably some time around 2005, and it’s likely that processor would have been in the Intel Core Duo family of chips. With a dual-core ESP32 now costing relative pennies it may be difficult to grasp in 2020, but there was a time when a multi-core processor was a very big deal indeed.

What if we were to tell you that there was another Intel dual-core processor back in the 1970s, and that some of you may even have owned one without ever realizing it? It’s a tale related to us by [Chris Evans], about how a team of reverse engineering enthusiasts came together to unlock the secrets of the Intel 8271.

If you’ve never heard of the 8271 you can be forgiven, for far from being part of the chip giant’s processor line it was instead a high-performance floppy disk controller that appeared in relatively few machines. An unexpected use of it came in the Acorn BBC Micro which is where [Chris] first encountered it. There’s very little documentation of its internal features, so an impressive combination of decapping and research was needed by the team before they could understand its secrets.

As you will no doubt have guessed, what they found is no general purpose application processor but a mask-programmed dual-core microcontroller optimized for data throughput and containing substantial programmable logic arrays (PLAs). It’s a relatively large chip for its day, and with 22,000 transistors it dwarfs the relatively svelte 6502 that does the BBC Micro’s heavy lifting. Some very hard work at decoding the RMO and PLAs arrives at the conclusion that the main core has some similarity to their 8048 architecture, and the dual-core design is revealed as a solution to the problem of calculating cyclic redundancy checks on the fly at disk transfer speed. There is even another chip using the same silicon in the contemporary Intel range, the 8273 synchronous data link controller simply has a different ROM. All in all the article provides a fascinating insight into this very unusual corner of 1970s microcomputer technology.

As long-time readers will know, we have an interest in chip reverse engineering.

source https://hackaday.com/2020/11/22/intels-forgotten-1970s-dual-core-processor/

Beer Pong Difficulty Level: 10

Beer pong is a fun enough game for those of a certain age, but one thing that it lacks is a way of cranking up the difficulty setting independent of the amount of beer one has consumed. At least, that was the idea [Ty] had when he came up with this automated beer pong table which allows the players to increase the challenge of this game by sliding the cups around the top of the table.

The build uses a belt-driven platform under a clear cover with a set of magnets attached. Each of the cups on the table has a corresponding magnet, which allows them to slide fairly easily back and forth on the table. The contraption is controlled by an Arudino Nano with a small screen and dial that allows the players to select a difficulty level from 1 to 10. The difficulty levels increase the speed that the cups oscillate on the table, which certainly adds another layer of complexity to this already challenging game.

While we hope to eventually see a beer pong table that can automatically arrange the cups as the game is played, we do appreciate the effort to make an already difficult game even more difficult. Of course, if you have problems with the difficulty level you might want to pick up a PongMate CyberCannon Mark III to help with those clutch beer pong shots.

source https://hackaday.com/2020/11/21/beer-pong-difficulty-level-10/

A Computer In The Game Of Life

We often hear the term “Turing-complete” without giving much thought as to what the implications might be. Technically Microsoft PowerPoint, Portal 2, and Magic: the Gathering all are Turing-complete, what of it? Yet, each time someone embarks on an incredible quest of perseverance and creates a computer in one of these mediums, we stand back in awe.

[Nicolas Loizeau] is one such individual who has created a computer in Conway’s Game of Life. Unlike electricity, the Game of Life uses gliders as signals. Because two orthogonal gliders can cancel each other out or form a glider eater if they intersect with a good phase shift, the basic logic gates can be formed from these interactions. This means the space between gates is crucial as signals need to be in phase alignment. The basic building blocks are a period-60 gun, a 90-degree glider reflector, a glider duplicator, and a glider eater.

All the Python code that generates these structures is on GitHub as the sheer size of the machine couldn’t possibly be placed by hand. The Python includes scripts to assemble the basic programs as a bank of selectable glider generators. It’s all based on Golly, which is an excellent program for simulating Conway’s Game of Life, among other things. While this isn’t the first computer in the Game of Life as [Paul Rendell] published a design in 2000 and [Adam Goucher] published a Spartan universal computer constructor in 2009, we think this is a particularly beautiful one.

The actual architecture has an 8-bit data bus, a 64-byte memory with two read ports, a ROM with 21 bits per line, and a one-hot encoded ALU supporting 8 different operations. Instructions have a 4-bit opcode which is decoding in a few different instructions. The clock is four loops, formed by the glider reflectors as the glider beams rotate. This gives the computer four stages: execution, writing, increment PC, and write PC to memory.

The Game of Life is an excellent example of Cellular Automaton (CA). There are several other types of CA’s and the history behind them is fascinating. We’ve covered this field before and delved into this beautiful fringe of computer science. Check out the video below to truly get a sense of the scale of the machine that [Nicolas] has devised.

source https://hackaday.com/2020/11/21/a-computer-in-the-game-of-life/

A Rocket Powered Ejection Seat For Model Aircraft

As radio control planes don’t typically have human pilots onboard, the idea of installing an ejection seat in one is somewhat frivolous. But that doesn’t mean it wouldn’t be a lot of fun, and [James Whomsley] has set his mind to achieving the task.

The build process is an iterative one, with [James] solving problems step-by-step and testing along the way. The first task was to successfully launch a small action figure and his flight seat vertically in a controlled fashion. After a few attempts, a combination of rocket motors and guide rails were settled upon that could achieve the goal. Next up, a drogue parachute system was designed and tested to stabilize the seat at the height of its trajectory. Further work to come involves handling seat separation and getting the action figure safely back to the ground.

While action figures aren’t alive and the ejection seat serves no real emergency purpose, we can imagine it would be a hit at the local flying field – assuming the parachutes don’t get tangled in someone else’s model. For those interested in the real technology, our own [Dan Maloney] did a great piece on the topic. Video after the break.

source https://hackaday.com/2020/11/21/a-rocket-powered-ejection-seat-for-model-aircraft/

Among Us Emergency Meeting Button Becomes Reality

Among Us has been an indie gaming success story. A game built by a small team has, after several years on the market, become a worldwide sensation. Gameplay consists of players attempting to find the imposter amongst their ranks and an “Emergency Meeting” can be called if players need to speak to each other. [john lemme] wanted to be able to do the same with his roommates, and set about building the real thing.

The build relies on an ESP32, which reads the state of a big red emergency button. When pressed, the ESP32 uses its WiFi connection to trigger a Discord conference call containing all the roommates. Naturally, it also plays the buzzer sound from the actual game, too – via a small amplifier and a speaker yanked from some headphones.

It’s a fun build, though [john] notes it has its limits. The call takes 10 seconds to initiate after the button press, and the audio hardware doesn’t do a great job of recreating the buzzer noise from the game. However, it’s a good starting point, and we think the concept could actually prove useful with some refinement. Video after the break.

source https://hackaday.com/2020/11/21/among-us-emergency-meeting-button-becomes-reality/

Why You Need to Finish

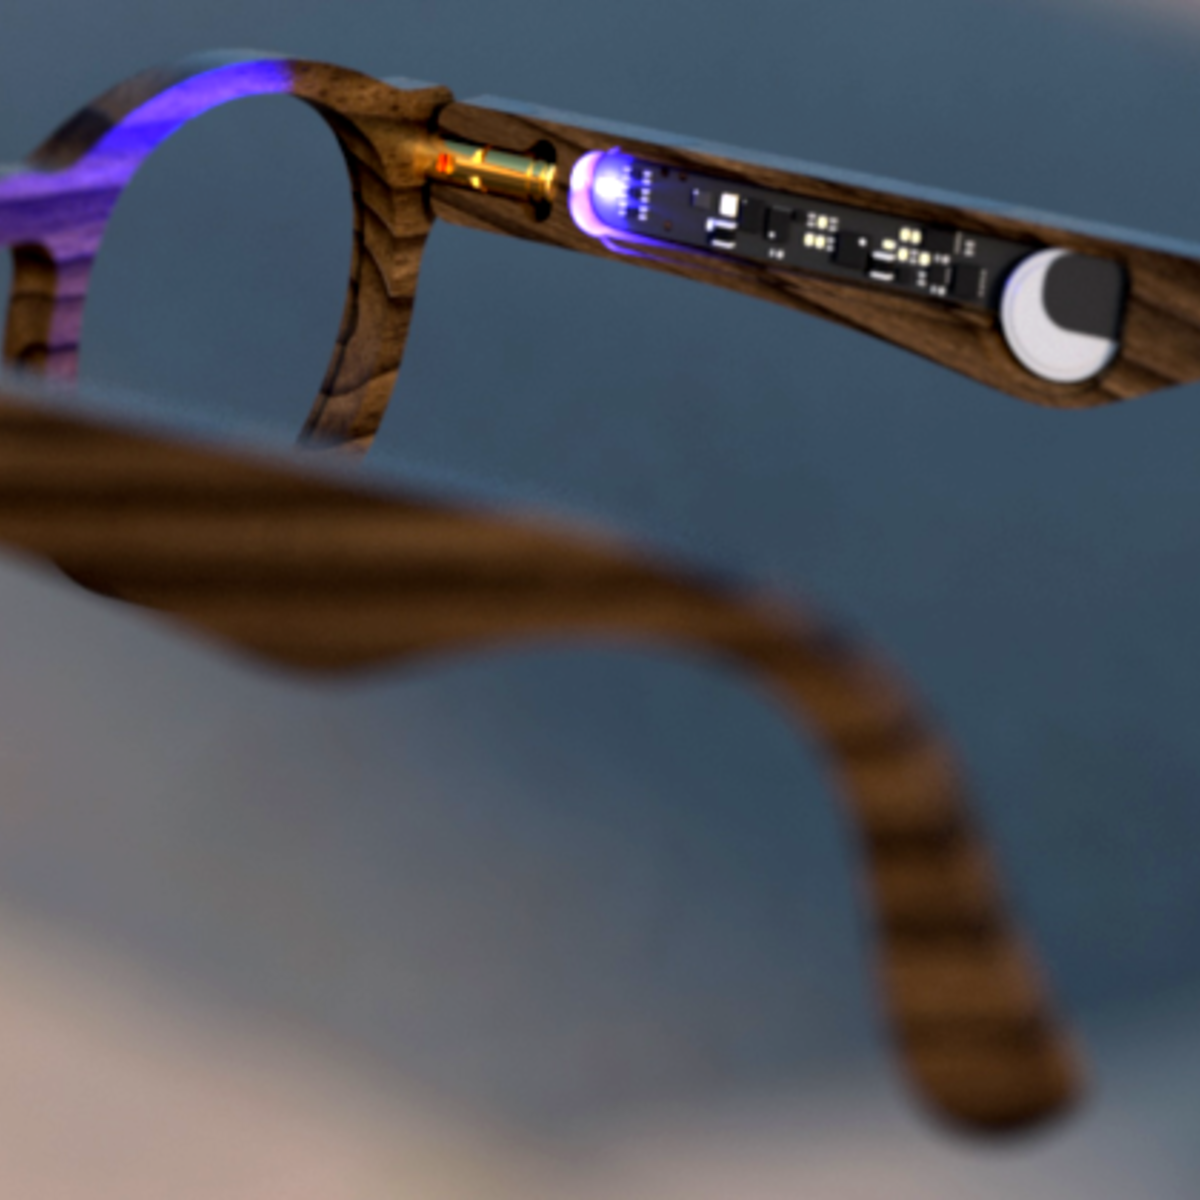
Mike and I were talking about an interesting smart-glasses hack on the podcast. This was one of those projects where, even if you don’t need a pair of glasses with LEDs on them to help you navigate around, you just couldn’t help but marvel at a lot of the little design choices made throughout.

For instance, I love the way the flex PCB is made to do double duty by wrapping around the battery and forming a battery holder. This struck me as one of those quintessential hacks that only occurs to you because you need it. Necessity is the mother of invention, and all that. There was a problem, how to fit a battery holder in the tiny space, and a set of resources that included a flex PCB substrate. Cleverly mashing that all together ended up with a novel solution. This wouldn’t occur to you if you were just sitting at the beach; you’d have to be designing something electronic, space-constrained, and on a flex PCB to come up with this.

Mike made an offhand comment about how sometimes you just need to finish a project for the good ideas and clever solutions that you’ll come up with along the way, and I think this battery holder example drives that point home. I can’t count the number of my projects that may or may not have been dumb in retrospect, but along the way I came up with a little trick that I’ll end up using in many further projects, outliving the original application.

Finishing up a project on principle is a reasonable goal just on its own. But when the process of seeing something to conclusion is the generator of new and interesting challenges and solutions, it’s even more valuable. So if you’re stuck on a project, and not sure you want to take it all the way, consider if the journey itself could be the destination, and look at it as an opportunity to come up with that next long-lasting trick.

Bad News: Arecibo

If you read the newsletter last week, you heard me wondering aloud if the damage to Arecibo Observatory had crossed the threshold into where it’s no longer economically viable to keep it running, and the sad news has just come in and the battle for Arecibo has been lost. We said we’d shed a tear, and here we are. Sic transit gloria mundi. Here’s hoping something cooler replaces it!

source https://hackaday.com/2020/11/21/why-you-need-to-finish/

Reduce, Reuse, Injection Mold

Many people have the means now to create little plastic objects thanks to 3D printing. However, injection molding is far less common. Another uncommon tech is plastic recycling, although we do occasionally see people converting waste plastic into filament. [Manuel] wants to solve both of those problems and created an injection molder specifically for recycling.

The machine — Smart Injector — is automated thanks to an Arduino. It’s pretty complex mechanically, so in addition to CAD models there are several PDF guides and a ton of pictures showing how it all goes together.

According to the documentation, the extrusion screw can provide 51 Nm of torque with a 48V supply using a NEMA34 stepper and a 6:1 gearbox. The machine can make an iPhone 8 cover in about 4 minutes and costs about  1000 Euro to build.

Of course, melting and extruding plastic isn’t the big trick. That lies in clamping the mold. That step is done with a threaded rod and a NEMA17 stepper. Then again, the other trick is developing your molds which need to have an ejection mechanism specific to the molded part.

While some people might be put off by the statement that the machine still needs some manual intervention due to unresolved clogging and clamping problems. We’ll bet that will be a challenge to Hackaday readers who will be happy to help resolve those issues.

If you build it, we’d love to hear about it. The project reminded us a lot of another iPhone case maker we saw a few years back, although some of the links there are dead. If you want to practice with something cheaper, try hot glue and some ingenuity.

source https://hackaday.com/2020/11/21/reduce-reuse-injection-mold/

Reverse Engineering a PokeWalker

The PokeWalker is part of Nintendo’s long quest to get children (and likely some adults) walking and exercising. There’s the PokeWalker, Pokemon Pikachu, PokeBall Plus, Pokemon Pikachu 2, Pokemon mini, and of course Pokemon Go. Despite being out a decade, there wasn’t a ROM dump for the device and there was minimal documentation on the communication protocol. [Dmitry Grinberg] took it upon himself to change all that and crack the PokeWalker open.

At its heart, the PokeWalker is just a pedometer with an IR port and a 96×64 grayscale screen. It came out in 2009 to accompany the new Pokemon release for the Nintendo DS. Cracking open the device revealed a 64KB EEPROM, a Renesas H8/38606R CPU, a Bosch BMA150 accelerometer, and a generic IR transceiver. The CPU is particularly interesting as in addition to being quite rare, it has a mix of 8, 16, and 32 bits with 24-bit pointers. This gives it a 64K address space. While the CPU is programmable, any attempt to do so erases the onboard flash. The communication protocol packets have an 8-bit header that precedes each packet. The header has a checksum, a command byte, and four bytes of session id, and an unused byte. Curiously enough, every byte is XOR’d with 0xAA before being broadcast.

One command is an EEPROM write, which uses back-referencing compression. Each chunk of data to be written is packaged into 128-byte chunks, though 128 bytes likely won’t be sent thanks to the compression. The command can theoretically reference 4k bytes back, but in practice, it can only reference 256 bytes back. It was this command that laid the foundation for the exploit. By carefully crafting the command to send, the command can overflow the decompression buffer and into executable code. Only a few bytes can be overflowed so the payload needs to be carefully crafted. This allowed for an exploit that reads the system ROM and broadcasts it out the IR port. Only 22k bytes can be dumped before the watchdog reboots the device. By changing the starting address, it was easy to do multiple passes.

After the ROM was stitched together from the different passes, the different IR commands were analyzed. In particular, a command was found that allows direct writes into RAM. This makes for a much easier exploit as you can write your exploit, then override a pointer in the event table, then have the exploit revert the event table once the system naturally jumps to your exploit.

[Dmitry] finishes off this amazing exploit by writing a PalmOS app to dump the ROM from a PokeWalker as well as modify the system state. PalmOS was chosen as it is an easy and cheap way to have a programmable IR transciever. All in all, a gorgeous hack with a meticulous writeup. This isn’t the first video game accessory that’s been reverse engineered with a scrupulous writeup, and we’re sure it won’t be the last.

Thanks to [schme16] for sending this one in!

[Featured Image: legandarypkmn.net and Arty2]

source https://hackaday.com/2020/11/21/reverse-engineering-a-pokewalker/

Big Nerf Bazooka Packs a Wallop

Nerf blasters are a fun toy, often confiscated from children once they hit one too many precious ornaments around the home in the midst of battle. [Ivan Miranda] is bigger than most children however, and set about building a much larger blaster.

The bazooka-like design uses a several meters of 160mm PVC pipe, firing “darts” constructed out of foam yoga rollers and buffing pads. The build uses a littany of 3D printed components in its construction, both as part of the firing mechanism and as jigs to help machine the pipe. A large plunger is used to propel the darts, which is pulled back against the tension of thick rubber tubes before being released by the trigger mechanism.

It’s an intimidating device, to be sure. However, we suspect its short range, huge size, and slow reload time should stop it from breaking the meta-game at your local Nerf battles. That said, we still wouldn’t want to take a shot from this bad boy to the head. Hackers do love a good Nerf build, and they’re particularly popular in sentry applications. Video after the break.

source https://hackaday.com/2020/11/20/big-nerf-bazooka-packs-a-wallop/

Procedurally Generated Trees

As the leaves fall from the trees here in the Northern Hemisphere, we are greeted with a clear view of the branches and limbs that make up the skeleton of the tree. [Nicolas McDonald] made a simple observation while looking at trees, that the sum of the cross-sectional area is conserved when a branch splits. This observation was also made by Leonardo Da Vinci (according to Pamela Taylor’s Da Vinci’s Notebooks). Inspired by the observation, [Nicolas] decided to model a tree growing for his own curiosity.

The simulation tries to approximate how trees spread nutrients. The nutrients travel from the roots to the limbs, splitting proportionally to the area. [Nicolas’] model only allows for binary splits but some plants split three ways rather than just two ways. The decision on where to split is somewhat arbitrary as [Nicolas] hasn’t found any sort of rule or method that nature uses. It ended up just being a hardcoded value that’s multiplied by an exponential decay based on the depth of the branch. The direction of the split is determined by the density of the leaves, the size of the branch, and the direction of the parent branch. To top it off, a particle cloud was attached at the end of each branch past a certain depth.

By tweaking different parameters, the model can generate different species like evergreens and bonsai-like trees. The code is hosted on GitHub and we’re impressed by how small the actual tree model code is (about 250 lines of C++). The power of making an observation and incorporating it into a project is clear here and the results are just beautiful. If you’re looking for a bit more procedurally generation in your life, check out this medieval city generator.

source https://hackaday.com/2020/11/20/procedurally-generated-trees/

A Motorized Rotary Shop Table from Scratch

As we’ve seen over the years, it’s possible to bootstrap your own metalworking shop using little more than a pile of scrap steel, a welder, and an angle grinder. With time and dedication, you can build increasingly complex shop tools until you’ve got yourself a nice little post-apocalyptic workshop. It’s the whole idea behind the [Workshop From Scratch] channel, and we never get bored of seeing his incredible backyard engineering.

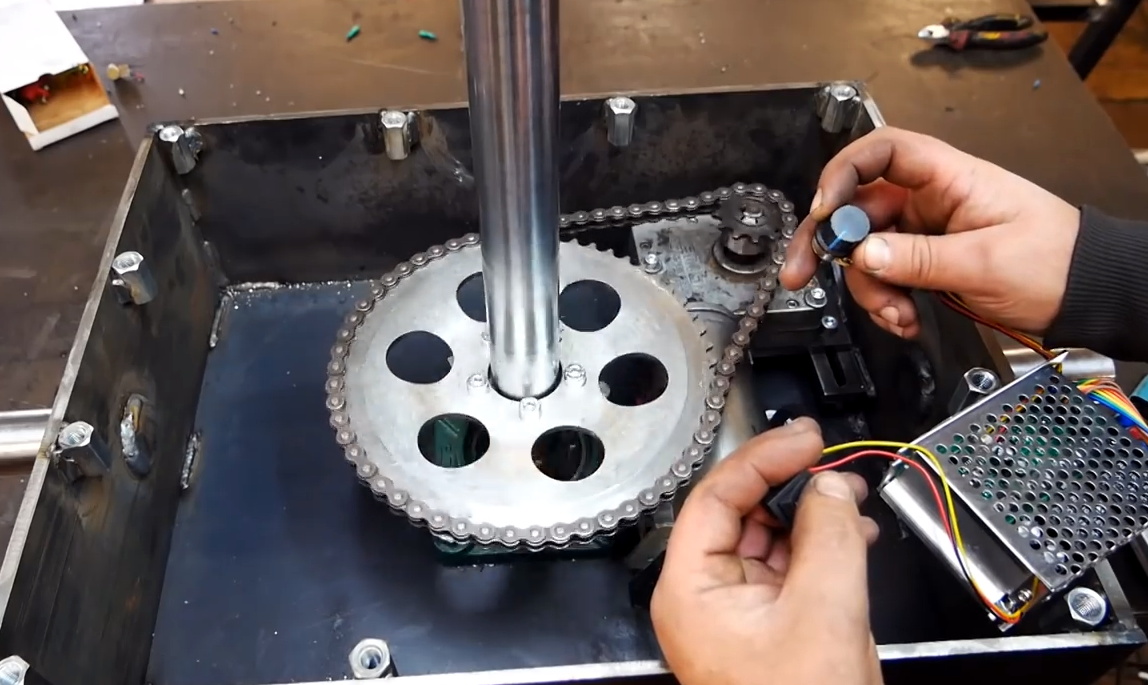
But eventually, you’ll have built all the basic stuff. What then? Well, as [Workshop From Scratch] shows in a recent video, you can start working on the luxuries. Do you need a motorized table that will let you spin the workpiece and position it an at arbitrary angle? No, probably not. But as the video after the break shows, it’s certainly a handy thing to have around the shop. We especially like how he uses it to quickly and easily produce nearly perfect circular welds.

Note the welded standoffs used to hold on the lid.

From a technical standpoint, this is perhaps one of his more straightforward builds. But at the same time, the attention to detail that he puts into even this “simple” design is phenomenal. Nothing is wasted, and cutoff pieces from one section are often used in imaginative ways elsewhere.

[Workshop From Scratch] is truly a master of working with what you have, and this project is a perfect example. We especially like the tilt mechanism, which uses a massive leadscrew spun by a wiper motor salvaged from an Audi A8 B4. It looks like a fair amount of new hardware went into the control electronics, but even still, we have no doubt that the cost of this build is well below the purchase price of a commercial alternative.

Much like his hydraulic lifting table or motorized plasma cutter, not everyone is going to need something this elaborate in their home shop. But his magnetic vise and mobile drill press cart are far more approachable for the home gamer. Of course even if you don’t follow along and build your own versions of his tools, it’s always worth tuning in just to see him work.

source https://hackaday.com/2020/11/20/a-motorized-rotary-shop-table-from-scratch/