
Monthly Archives: January 2020
16 ALIEXPRESS REVIEW COOL TOOLS (2019) | AMAZING TOOLS. ELECTRONICS. THINGS.
OpenDog: Adding Force Sensitive Feet
[James Bruton] OpenDog remains one of the most impressive home-built robotics projects we’ve seen here on Hackaday, and it’s a gift that just keeps on giving. This time he’s working on adding force sensing capabilities to OpenDog’s legs to allow for more dynamic movement control.
The actuators in the legs are three-phase outrunner motors that drive ball-screws via a belt. This configuration is non-backdrivable, meaning the legs cannot be moved when an external force is, which could lead to mechanical failures. He as tested other backdrivable leg configurations with other robots, but did not want to rebuild OpenDog completely. The solution [James] went with is a redesigned foot with an inbuilt switch, to confirm that the foot is touching the ground, and a load cell attached in the middle of the bottom leg segment. The load cell is bolted rigidly onto the leg segment, which allows it to sense when the leg is carrying load, without damaging the load cell itself.
Unfortunately all the serial ports on OpenDog’s main Teensy 3.6 controller are already used, so he converted the signal from the load cell to PWM, to allow it to be read by a normal GPIO pin. This works well in isolation, but when [James] switches on the motors, the PWM signal from the load sensor gets flooded by interference, making it unreadable. To solve this problem, he wants to implement a CAN bus, which will allow for more inputs and outputs and hopefully solve the interference problem. However, [James] has no experience with the CAN protocol, so learning to use it is going to be a project on its own.
OpenDog is turning into a very lengthy, time-consuming project, [James] says that the lessons learned from it have been invaluable for a number of other projects. This is something to keep in mind with everything we tackle. Choose projects were the experience gained and/or relationships developed are worth it on their own, even when the project fails in a conventional sense. This way you can never really lose.
source https://hackaday.com/2020/01/04/opendog-adding-force-sensitive-feet/
Making a Custom Caliper Case for Pros
Every professional has a tool set that they would never part with. Likewise, for experimental physicists, mechanical engineers, and tinkerers, a caliper set can be unspeakably crucial to their work. That’s why [Andrew Birkel] designed his own personal caliper set to fit just the right proportions for his tools while adding a bit of personal flair.
The project uses CNC routing, Solidworks for CAD, laser engraving, and woodworking to design the custom case for a set of calipers, metric and English screw pitch gauges, fillet gauges, and radius gauges. It’s a practical build for a custom tool set that doesn’t already come with a case of its own. The particular tools were chosen for their use in particle physics experiments: for determining threads, inside and outside curvatures, and measuring length, depth, and width.
The box was made from an oversized piece of wood with holes drilled into the sides. After compiling the G-code program for the build, the two halves of the box was was milled from the wood. The first run on the CNC mill with aluminum managed to cause the grain to split, so [Birkel] went with a CNC router instead. Once the piece was sanded, hidden barrel hinges were added. The finished box was wiped down with mineral oil and teak oil to bring out the natural coloration of the wood as well as to add protection (lacquer mixed into the oil). To finish it off, the case was customized with a laser engraved name and email for identification.
It’s a pretty slick build to say the least, and certainly one that can be customized to the dimensions of whatever tools your personal caliper set happens to have.
source https://hackaday.com/2020/01/04/making-a-custom-caliper-case-for-pros/
Dinural Reef Control Realistically Insolates Your Aquarium
[Phillip]’s project is not just great for learning new words, it also shows just how complex natural systems can be.
As we know from news around the word, reefs are delicate systems prone to damage from just about any imaginable threat. Escaped aquarium fish, sunscreen, and the wayward feet of well meaning tourists to name a few. So it’s no wonder that aquarium hobbyists sometimes go to incredible lengths to simulate the natural environments these creatures live in.
While [Phillip] is still tinkering with his designs for this project, we found the data he included really interesting. His goal is to be able to plug in any coordinate on the earth and have the lights replicate the location. That includes not just the sun, but also the light from the moon as many corals seem to only spawn during certain tides. Of course no LED is perfect so he’s even experimenting with putting light sensors under the water to provide a feedback loop to make it perfect.
We really like the ambition of this project and we hope he continues.
source https://hackaday.com/2020/01/03/dinural-reef-control-realistically-insolates-your-aquarium/
Steve Joins A Girl’s School
Amazing EDC Gadgets For the Modern Gentleman
Creative DIY Ideas That Will Take Your Home To The Next Level ▶7
r/prorevenge | I Banned my Employer from the USA and cost them $50,000…
r/NuclearRevenge – I Got My Boss Deported…He Paid the ULTIMATE Price.
Tracking Vaccination History With Invisible Tattoos
Nowadays, we still rely on medical records to tell when our last vaccinations were. For social workers in developing countries, it’s an incredibly difficult task especially if there isn’t a good standard in place for tracking vaccinations already.
A team at the Massachusetts Institute of Technology may be providing a solution – they’ve developed a safe ink to be embedded into the skin alongside the vaccine, only visible under a special light provided by a smartphone camera app. It’s an inconspicuous way to document the patient’s vaccination history directly into their skin and low-risk enough to massively simplify the process of maintaining medical records for vaccines.
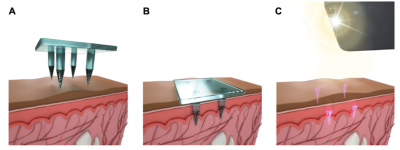
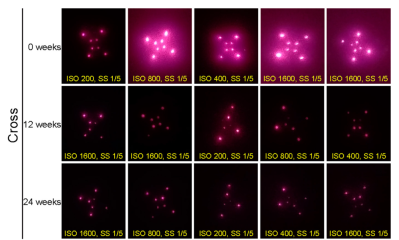
The tatoo is made up of tiny quantum dots – semiconductor crystals that reflect light – that glow under infrared light. The pattern is delivered using dissolving microneedles made up of polymers and sugar. While the solution remains in the proof-of-concept stage, the researchers were successfully able to detect patterns embedded into the skins of rats nine months after the initial injection. On human cadavers, the patterns remained identifiable after five years of simulated sun exposure.
This could certainly mean new possibilities for decentralized information delivery and storage. Alongside biodegradable implants and power pills, we could be looking at an exciting frontier for biohacking.
source https://hackaday.com/2020/01/03/tracking-vaccination-history-with-invisible-tattoos/
Voltmeter Clock Looks Great On Display
Voltmeters are cheap, and have a great industrial aesthetic about them. This makes them prime candidates for hackers looking to do a clock build. [Brett Oliver] went down this very road, and built a very stylish timepiece along the way.
[Brett] initially wanted to go with 240-degree voltmeters, however the cost was prohibitive, so settled for the more common 90-degree models. New dials were produced by first sanding down the old dials, repainting in an old-fashioned off-white, and then applying the new graphics with inkjet transfer paper.
The attention to detail continues with the case. [Brett] aimed to build the clock with an old-school lab equipment aesthetic. A large piece of mahogany was crafted into the base. A clear plastic cover was sourced from eBay, which really makes the piece. Large buttons and toggle switches were chosen to complete the look.
On the electronic side of things, it’s all run by a PIC16F628A, which controls the voltmeters via PWM. Running with a 20MHz crystal, the PIC is not a great timekeeper. Instead, the whole show is synchronized to [Brett]’s master clock we featured a few years back.
Building a clock is a rite of passage for a hacker, and [Brett]’s example goes to show how craftsmanship can really pay off in this pursuit. Video after the break.
source https://hackaday.com/2020/01/03/voltmeter-clock-looks-great-on-display/
Unique 3D Printer Turned CNC Engraver
As we’ve said in the past, one of the most exciting things about the proliferation of low-cost desktop 3D printers (beyond all the little boats we get to see on Reddit), is the fact that their motion control systems are ripe for repurposing. Outfitting a cheap 3D printer with a drag knife, pen holder, or even a solid-state laser module, are all very common ways of squeezing even more functionality out of these machines.
But thanks to the somewhat unusual nature of his printer, [Hammad Nasir] was able to take this concept a bit farther. Being considerably more rigid than the $99 acrylic-framed box of bolts we’ve become accustomed to, he was able to fit it with a basic spindle and use it for CNC engraving. He won’t be milling any steel on this rig, but judging by the pictures on the Hackaday.io page for the project, it does a respectable job cutting designs into plastic at least.
 The IdeaWerk 3D printer that [Hammad] used for this project is phenomenally overbuilt. We don’t know whether the designers simply wanted to make it look futuristic and high-tech (admittedly, it does look like it could double as a movie prop) or they thought there was a chance it might get thrown down the stairs occasionally. In either event, it’s built like an absolute tank.
While the frame on lesser printers would likely flex as soon as the bit started moving across the workpiece, this thing isn’t going anywhere. Of course this machine is presumably still running on the standard GT2 belt and NEMA 17 arrangement that has been used in desktop 3D printers since the first wooden machines clattered to life. So while the frame might be ready to take some punishment, the drive system could respectfully disagree once the pressure is on.
Modification was simplified by the fact that the hotend and extruder assembly on the IdeaWerk is mounted to the X axis with just a single bolt. This makes it exceptionally easy to design alternate tool mounts, though arguably the 3D printed motor holder [Hammad] is using here is the weak link in the entire system; if it’s going to flex anywhere, it’s going to be there.
If you’re more photonically inclined, you might be interested in this similarly straightforward project that sees a 2.5 W laser module get bolted onto an entry level 3D printer.
source https://hackaday.com/2020/01/03/unique-3d-printer-turned-cnc-engraver/
First Q&A!!
You Could be a Manufacturing Engineer If You Could Only Find the Time
Let’s be honest, Ruth Grace Wang can’t teach you how to be a manufacturing engineer in the span of a twenty minute talk. But no-one can. This is about picking up the skills for a new career without following the traditional education path, and that takes some serious time. But Grace pulled it off, and her talk at the 2019 Hackaday Superconference shares what she learned about reinventing your career path without completely disrupting your life to do so.
Ruth got on this crazy ride when she realized that being a maker made her happy and she wanted to do a lot more of it. See wanted to be “making stuff at scale” which is the definition of manufacturing. She took the hacker approach, by leveraging her personal projects to pull back the veil of the manufacturing world. She did a few crowd funding campaigns that exposed her to the difficulties of producing more than one of something. And along the way used revenue from those projects to get training and to seek mentorships.
Those mentorships can come in many forms. Much of her success stems from the personal connections she made at conferences, through online interactions, and at Noisebridge, her local hackerspace in San Francisco. One of the most interesting stories she mentions is a mentorship hack where she found people with the skills she wanted to learn, and convinced them to give a class about it if she did all the organizational legwork.
She had begun to learn Mandarin when the opportunity to start working on a manufacturing project with a startup came along. But her skills acquisition phase never ended. Ruth advocates for personal curiosity, and used her own as radar to pick up on new things to learn that others may have missed.
But what we all might benefit from most in this talk is her discussion at the end about finding time. Ruth says “your productivity will never increase”, because productive people are already using their available time. That doesn’t mean you can’t pick up new career skills on the side. But it does mean you need to throw some things overboard. From showing up late, to adopting a clean clothes box, Ruth certainly dipped into the well of life hacks to get there. She succeeded, and two years after the original epiphany she’s finally landed a job as a manufacturing engineer.
The Quadratic Equation Solution a Few Thousand Years in the Making
Everyone learns (and some readers maybe still remember) the quadratic formula. It’s a pillar of algebra and allows you to solve equations like Ax2+Bx+C=0. But just because you’ve used it doesn’t mean you know how to come up with the formula itself. It’s a bear to derive so the vast majority of us simply memorize the formula. A Carnegie Mellon mathematician named Po-Shen Loh didn’t expect to find a new way to derive the solution when he was reviewing math materials for middle school use to make them easier to understand. After all, people have been solving that equation for about 4,000 years. But that’s exactly what he did.
Before we look at the new solution, let’s talk about why you want to solve quadratic equations. They are used in many contexts. In ancient times you might use them to determine how much more crop to grow to cover pay tax payments without eating in to the crop you needed to subsist. In physics, it can describe motion. There’s seemingly no end to how many things you can describe with a quadratic equation.
Babylonians, in particular, would solve simultaneous equations to find the roots of a quadratic. Egyptians, Grecians, Indians, and Chinese peoples used graphical methods to solve the equations. The entire history is a bit much to get into, but still a great read. For this article, let’s dig into how the new derivation was discovered.
Setting Up the Equation
So what’s the method? You watch Loh explain it himself in the video, below. Suppose you have a standard quadratic equation for whatever reason that looks like this:
x2-6x+3=0
In this case, A=1, B=6, and C=3. Note that for Loh’s method to work, A should equal 1, but if it doesn’t you can always divide both sides by A to make that true. For example, consider this equation:
3x2-18x+9=0
It will have the same roots as the first one because if you divide both sides by 3, you get the first equation.
The Polynomial Factor
To factor a polynomial into two binomials we can use FOIL (First/Inner/Outer/Last). So we know that:
x2-6x+3=(x-S)(x-R)
Where we just made up S and R. They exist, but we don’t know what they are yet. However, for the answer to be zero, you can see that the equation will be zero when x=S or X=R so that means S and R are the roots of the equation.
So What’s S and R?
It sounds silly, but let’s multiply out the binomials into another polynomial. Remember FOIL:
x2-6x+3=x2-(S+R)x+SR
If you look at that for a second, you will probably realize that S times R must be 3. We also know they add up to 6. At this point, you can probably just guess the roots, but let’s make it formal.
The roots of a polynomial like this will be in the form of U±z. So if S=U+z and R=U-z, the only way to make (U+z)+(U-z) equal to 6 is if U is 6/2. Since B is -6 in this example, we can intuit that U must be -B/2 in the general case.
Home Stretch
So we now know the roots are -B/2+z and -B/2-z. We know that B is -6. We also know the answer is when we multiply those roots together must be C (3, for our example). So we can write:
(-(-6)/2+z)(-(-6)/2-z)=3
Or:
(3+z)(3-z)=3
Do the FOIL method again and get:
9+3z-3z-z2=3
The middle terms will always cancel out so you get:
9-z2=3
Subtract 3 from both sides and add z squared to both sides:
6=z2
Since the root must be -B/2±z we know that our two roots are 3+√6 and 3-√6.
The Key and the Catch
The point is, none of this was hard to remember or work out. Just remember that you rewrite the zero as (x-S)(x-R) and the rest follows very logically.
The only real problem is not many quadratic equations have A=1. For example, suppose you throw a ball straight up from 5 meters above the ground with a velocity of 15 m/s. We want to know when the ball will hit the ground.
Gravity is going to pull down on the ball at about 4.9 meters per second squared (assuming gravity accelerates at -9.8 m/s2). The physics formula is (at2)/2 so we get our first term of -4.8t2. The second term will represent the speed of the ball which is simply 15t. We also started 5 meters above the ground, so we will add 5 and wind up with:
-4.8t2+15t+5
This formula will tell you where the ball is assuming you throw at t=0. We want to know when it hits the ground so that will be one of the roots:
-4.8t2+15t+5=0
To use the new method, just divide it all through by -4.8 to get:
t2-3.125t-1.04=0
So now B=-3.125 and C=-1.04. We know the root will be -B/2±z or 1.5625 and that z2 will equal (1.5625)2+1.04.
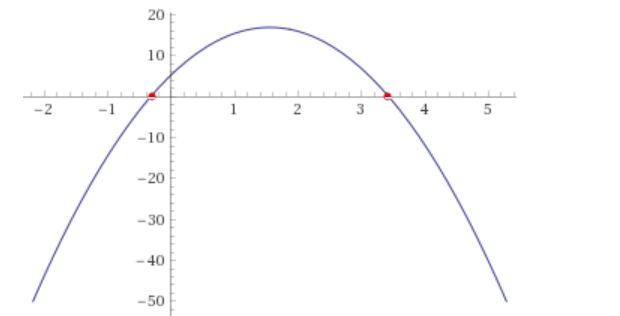 That’s 3.48 (about) and the square root is about 1.866. The roots, then, are 1.5625±1.866. Working that out, we get -0.30 and 3.4285. The negative root is nonsense in this case but the ball will land almost 3.5 seconds after you throw it.
If you don’t trust our work, ask Wolfram Alpha or plug 3.4285 back into the original formula. Wolfram says 3.43 and the check your own work says 0.005 meters at that time, so given that I rounded a few times, that’s pretty close. Besides, I’m ignoring things like air resistance. This specific calculator says 3.36 seconds, which is still pretty close.
In Summary
If you prefer things in algorithmic steps, here you go:
- Find A, B, and C for the quadratic equation.
- If necessary, divide by A so that A now is 1.
- Write
-(B/2)2-z2=C - Solve for z (since you know B and C)
- Roots are
-B/2±z
Everything Old is New Again
We get it. Many people may have figured this out before. But if they did, they apparently forgot to share it with anyone in any permanent form. If you read the actual paper, you’ll see how easy it is to symbolically derive the “old” standard formula. Compare that to the traditional method. If you read the proof, it seems simple enough, but go back in a few weeks and try to work it out yourself. Not so easy. This is also much easier to remember even if you don’t want to derive it every time.
Of course, making A=1 is part of the trick. It is well known, for example, that the product of the roots of a quadratic is C/A. Since we know A=1, it follows that the product of S and R are also C, using this method. Normalizing A to 1 is also an old trick and is sometimes called a reduced quadratic equation. However, it doesn’t look like anyone put all the pieces together until now.
If you don’t like Wolfram Alpha, there’s always Mathics (hint: use Solve[-4.8t^2+15t+5==0,t]). There are also specific calculators. Or just bite the bullet and keep everything in a Jupyter Notebook.
source https://hackaday.com/2020/01/03/the-quadratic-equation-solution-a-few-thousand-years-in-the-making/
Hackaday Podcast 048: Truly Trustworthy Hardware, Glowing Uranium Marbles, Bitstreaming the USB, Chaos of Congress
 Hackaday editors Elliot WIlliams and Mike Szczys kick off the first podcast of the new year. Elliot just got home from Chaos Communications Congress (36c3) with a ton of great stories, and he showed off his electric cargo carrier build while he was there. We recount some of the most interesting hacks of the past few weeks, such as 3D-printed molds for making your own paper-pulp objects, a rudimentary digital camera sensor built by hand, a tattoo-removal laser turned welder, and desktop-artillery that’s delivered in greeting-card format.
Take a look at the links below if you want to follow along, and as always tell us what you think about this episode in the comments!
Direct download (69 MB)
Places to follow Hackaday podcasts:
Episode 048 Show Notes:
New This Week:
Interesting Hacks of the Week:
- 3D Printing Paper — Sort Of
- 194 LED Ball Is Free-Form Soldering On Another Level
- VGA Signal In A Browser Window, Thanks To Reverse Engineering
- 36C3: Open Source Is Insufficient To Solve Trust Problems In Hardware
- Roll The Bones Chernobyl Style
- Image Sensor From Discrete Parts Delivers Glorious 1-Kilopixel Images
- Alex’s Tiny LED Matrices
Quick Hacks:
- Elliot’s Picks:
- Mike’s Picks:
Can’t-Miss Articles:
- Ask Hackaday: How Do You Keep The 3D Printer From Becoming EWaste
- 2019: As The Hardware World Turns
- Greg Davil’s FPGA Designs (OrangeCrab and ArcticKoala)
- Mozilla’s Deep Speech implementation
The Fun is On the Christmas Tree with This Playable Duck Hunt Decoration
‘Tis the season for leftovers, be they food, regifted presents, or the decorations left behind in the wake of the festivities. Not to mention the late tips we get for holiday-themed builds, like this Duck Hunt ornament that’s completely playable.
Details are sparse in [wermy]’s video below, but there’s enough there to get the gist. The game is based on the Nintendo classic, where animated ducks fly across the screen and act as targets for a light pistol. Translating that to something suitable for decorating a Christmas tree meant adding an Arduino and an IR LED to the original NES light pistol, and building a base station with a Feather and a small LCD screen into a case that looks like [The Simpsons] TV. An LED on each 3d-printed duck target lights in turn, prompting you to blast it with the gun. An IR sensor on each duck registers hits, while the familiar sound effects are generated by the base, which also displays the score. Given a background of festive blinkenlights, it’s harder than it sounds – see it in action briefly below.
[wermy] has done some interesting builds before, like a RetroPie in an Altoids tin and a spooky string of eyes for Halloween. We hope he’ll come through with a more detailed build video for this project at some point – we’re particularly interested in those beautiful multi-color 3D-prints.
[via sudomod]
This Week in Security: ToTok, Edgium, Chrome Checks your Passwords, and More
Merry Christmas and happy New Year! After a week off, we have quite a few stories to cover, starting with an unexpected Christmas gift from Apple. Apple has run an invitation-only bug bounty program for years, but it only covered iOS, and the maximum payout topped out at $200K. The new program is open to the public, covers the entire Apple product lineup, and has a maximum payout of $1.5 million. Go forth and find vulnerabilities, and make sure to let us know what you find.
ToTok
The United Arab Emirates had an odd policy regarding VoIP communications. At least on mobile networks, it seems that all VoIP calls are blocked — unless you’re using a particular app: ToTok. Does that sound odd? Is your “Security Spider Sense” tingling? It probably should. The New York Times covered ToTok, claiming it was actually a tool for spying on citizens.
While that coverage is interesting, more meat can be found in [Patrick Wardle]’s research on the app. What’s most notable, however, is the distinct lack of evidence found in the app itself. Sure, ToTok can read your files, uploads your contact book to a centralized server, and tries to send the device’s GPS coordinates. This really isn’t too far removed from what other apps already do, all in the name of convenience.
It seems that ToTok lacks end-to-end encryption, which means that calls could be easily decrypted by whoever is behind the app. The lack of malicious code in the app itself makes it difficult to emphatically call it a spy tool, but it’s hard to imagine a better way to capture VoIP calls. Since those articles ran, ToTok has been removed from both the Apple and Google’s app stores.
SMS Keys to the Kingdom
Have you noticed how many services treat your mobile number as a positive form of authentication? Need a password reset? Just type in the six-digit code sent in a text. Prove it’s you? We sent you a text. [Joakim Bech] discovered a weakness that takes this a step further: all he needs is access to a single SMS message, and he can control your burglar alarm from anywhere. Well, at least if you have a security system from Alert Alarm in Sweden.
The control messages are sent over SMS, making them fairly accessible to an attacker. AES encryption is used for encryption, but a series of errors seriously reduces the effectiveness of that encryption. The first being the key. To build the 128-bit encryption key, the app takes the user’s four-digit PIN, and pads it with zeros, so it’s essentially a 13 bit encryption key. Even worse, there is no message authentication built in to the system at all. An attacker with a single captured SMS message can brute force the user’s PIN, modify the message, and easily send spoofed commands that are treated as valid.
Microsoft Chrome
You may have seen the news, Microsoft is giving up on their Edge browser code, and will soon begin shipping a Chromium based Edge. While that has been a source of entertainment all on its own, some have already begun taking advantage of the new bug bounty program for Chromium Edge (Edgium?). It’s an odd bounty program, in that Microsoft has no interest in paying for bugs found in Google’s code. As a result, only bugs in the Edge-exclusive features qualify for payout from Microsoft.
As [Abdulrahman Al-Qabandi] puts it, that’s a very small attack surface. Even so, he managed to find a vulnerability that qualified, and it’s unique. One of the additions Microsoft has made to Edgium is a custom new tab page. Similar to other browsers, that new tab page shows the user their most visited websites. The problem is that the site’s title is shown on that page, but without any sanity checking. If your site’s title field happens to include Javascript, that too is injected into the new tab page.
The full exploit has a few extra steps, but the essence is that once a website makes it to the new tab page, it can take over that page, and maybe even escape the browser sandbox.
Chrome Password Checkup
This story is a bit older, but really grabbed my attention. Google has rolled a feature out in Chrome that automatically compares your saved passwords to past data breaches. How does that work without being a security nightmare? It’s clever. A three-byte hash of each username is sent to Google, and compared to the hashes of the compromised accounts. A encrypted database of potential matches is sent to your machine. Your saved passwords, already encrypted with your key, is encrypted a second time with a Google key, and sent back along with the database of possible matches, also encrypted with the same Google key. The clever bit is that once your machine decrypts your database, it now has two sets of credentials, both encrypted with the same Google key. Since this encryption is deterministic, the encrypted data can be compared without decryption. In the end, your passwords aren’t exposed to Google, and Google hasn’t given away their data set either.
The Password Queue
Password changes are a pain, but not usually this much of a pain. A university in Germany suffered a severe malware infection, and took the precaution of resetting the passwords for every student’s account. Their solution for bootstrapping those password changes? The students had to come to the office in person with a valid ID to receive their new passwords. The school cited German legal requirements as a primary cause of the odd solution. Still, you can’t beat that for a secure delivery method.
HoloLens Brings Video Game Kart Racing to Life
There aren’t a lot of video game experiences we can easily recreate in the physical realm. You’ll quickly find that jumping on mushrooms in the real world doesn’t have nearly the same appeal as it does in Super Mario, and we won’t even get into the dangers of trying to recreate Frogger on your local multi-lane. But video game style go-kart racing? We have all the technology to pull that off, somebody just has to put all the pieces together.
Which is precisely what [Ian Charnas] is trying to do with his latest project. Using Microsoft’s HoloLens augmented reality headset, electric go-karts, 433 MHz wireless transceivers, and some Arduinos sprinkled in, he’s created the closest thing to Mario Kart that us flesh and blood mortals are likely to experience anytime soon.
 The HoloLens headset worn by each driver overlays the necessary graphical elements like pickups and weapon effects, as well as puts over-the-top cartoon heads on the other racers. But of course, that’s only half of the story. Seeing the pickups and gadgets doesn’t do you any good if they don’t have any effect on the actual race.
To that end, [Ian] has come up with a way to control the performance of the go-karts using an electronic “backpack” that mounts to each kart. So speed boosting pickups actually make the kart go faster, and if a driver gets hit with a weapon fired at them, they get slowed down.
That’s the high-level version, anyway. There’s obviously a lot going on behind the scenes, some of which are detailed on the Hackaday.io page. One of the interesting notes is that the HoloLens needs visual markers to orient itself, which in the video after the break can be seen as black and white posters dotting the walls alongside the track. As the project progresses, [Ian] is hoping that these can be camouflaged in creative ways (such as being made to look like audience members or checkered flags) to make the overall experience more immersive.
According to [Ian], the next step is to find partners who want to help elevate this from a one-off project to something that you might actually see at an amusement park. We wish him luck, if for no other reason than we really want to play the thing ourselves. In the meantime, we’ll have to settle for racing hacked Power Wheels.
source https://hackaday.com/2020/01/03/hololens-brings-video-game-kart-racing-to-life/
A Programming Language That Lets You Code With Pixels
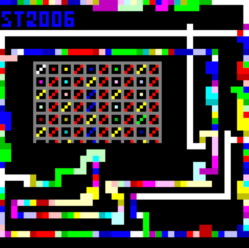
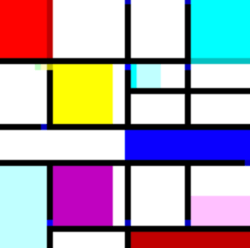
This programming language gives you programs that resemble modern art. It’s fortunately a feature of the language, dubbed Piet after the famed abstract painter Piet Mondrian.
The language uses 20 distinct colors, with the colors cycling from red to yellow to green to cyan to blue to magenta and the lightness cycling from light to normal to dark. The code is formed from graphics made of the recognized colors, with individual pixels holding much of the information. Stacks are used for storing data values, that can exist as integers or as Unicode characters with the proper commands applied.
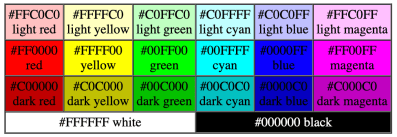
Numbers in the program are represented by colors, while black blocks indicates edges and white blocks indicate free zones. The interpreter physically slides through blocks in the direction of the Direction Pointer (DP), with hue changes indicating different commands based on the steps of the change.
To execute a program, the Piet language interpreter begins in the upper left codel (or individual code block) of the program, maintaining a DP initially pointed to the right and a Codel Chooser (CC) initially pointed to the left. The DP and CC turn right, left, down, or up depending on the execution.
There is currently a small community of coders developing sample programs, interpreters, IDEs, and compilers for the language. You can check out some of the sample programs here.
source https://hackaday.com/2020/01/03/a-programming-language-that-lets-you-code-with-pixels/
Prolific Videos Show Altair 8800 Recreation
The January 1975 issue of Popular Electronics introduced the Altair 8800 and hit the newsstands in December of 1974, so it is only natural that around the New Year people start thinking about the old computer. [Shadowtron] did more than think about it. He ordered some replica PCBs and is building a new one. Even better, he’s posted an amazing number of videos (up to number 56 as I write this) detailing his progress. You can find part 1, below.
The boards are from Trailing Edge Technology. There’s a backplane board (about $100) as well as a few boards to fit it available for about $30 each — unpopulated, of course.
We’ll confess we haven’t watched all 56 videos yet. They cover the construction of the CPU and front panel, the serial I/O board, floppy drives, software, and a homebrew EPROM board (using 1702s, no less).
I have to confess, I’ve always wanted a real Altair — but probably won’t ever get one. But if I were going to build one, this would be the guide to watch as it covers just about everything.
Of course, there are replicas (I have a few and even helped develop one). Plus you can run a great simulation on your PC or even in a browser. But there’s something about knowing you have the real deal — or as close as you can get to it — that makes an intangible but real difference.
source https://hackaday.com/2020/01/02/prolific-videos-show-altair-8800-recreation/